

More than 9 million Android smartphones are running malicious applications that are downloaded from the app store of Huawei, AppGallery.
The cybersecurity experts at Doctor Web security firm have recently found nearly 200 games with “Android.Cynos.7.origin” Trojan inside them, and it’s one of the alterations of the Cynos program module.
This “Android.Cynos.7.origin” trojan is found in 190 games that have download counts of approximately 9,300,000. This Trojan is specifically designed to get data like mobile phone numbers and other data to distribute to their developers.
Data Collected
All these malicious games are primarily aimed at children since they are the easy targets to get enabled all their permission. Now, once the user grants permission, this trojan collects and sends all the following data to a remote server:-
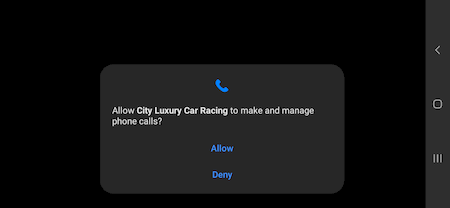
- User mobile phone number
- Device location based on GPS coordinates or the mobile network and Wi-Fi access point data.
- Various mobile network parameters like: network code, mobile country code, GSM cell ID, international GSM location area code.
- Various technical specs of the device.
- Various parameters from the trojanized app’s metadata.
The “[Android.Cynos.7.origin]” malware is a modification of the original Cynos, and it’s been active since 2014. This malware also has the ability to download and install other apps and modules on compromised devices.
Affected Apps
Currently, all the affected games have been removed by Huawei from its apps store, AppGallery. But, if you have a Huawei device and you are not sure that you are infected or not, then you can check the list of all the affected games below:-
- “[Команда должна убить боеголовку]” with more than 8000 installs.
- “Cat game room” with more than 427000 installs.
- “Drive school simulator” with more than 142000 installs.
- “[快点躲起来]” with more than 2000000 installs.
If you want the full list of affected apps then you can click here. Moreover, Huawei has already been notified by the Doctor Web malware analysts about these malicious apps.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates.






