

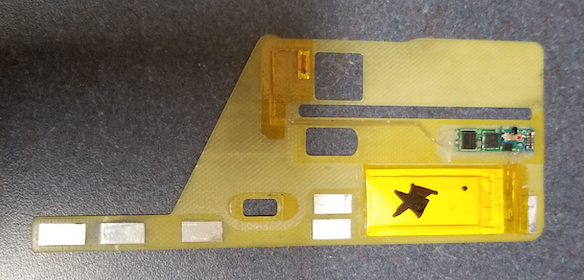
It has been reported that in New York City a number of financial institutions are facing an outburst of super-thin skimming devices known as “deep inserts”. In this type of skimming device, the card is inserted into the mouth of a slot on the ATM that accepts cards.
As a clever disguise, the card skimmers are paired up with pinhole cameras that are hidden within the cash machine in order to pose as part of that machine.
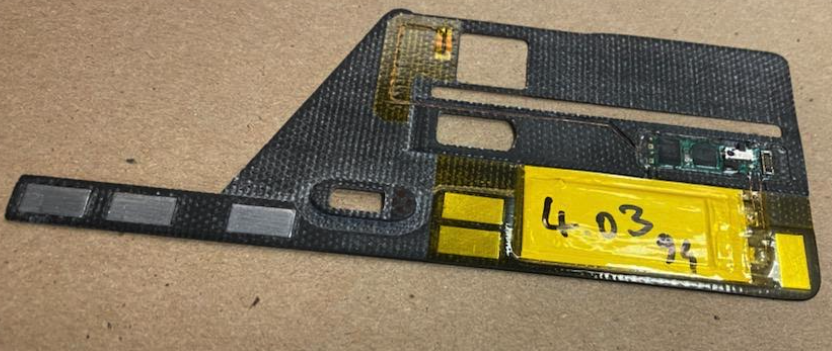
Approximately .68 millimeters is the height of the insert skimmer. It is important to note that this is plenty of space for the machine to capture and return the customer’s credit or debit card without interrupting the machine’s ability to retrieve the card.
Chip-card data or transactions are not snatched by these skimmers. However, most payment cards issued to American citizens still contain plain text cardholder data stored on the magnetic stripe.
Also Read: ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities
Threat Actors’ Goal
In designing this skimmer, the thieves specifically sought the data stored on the magnetic stripe and the 4-digit PIN of the customer.
According to the Kerbs investigation report, With those two pieces of data, the crooks can then clone payment cards and use them to siphon money from victim accounts at other ATMs. ATMs made by NCR, called SelfServ 84 Walk-Up were abused by the threat actors to install these skimming devices.
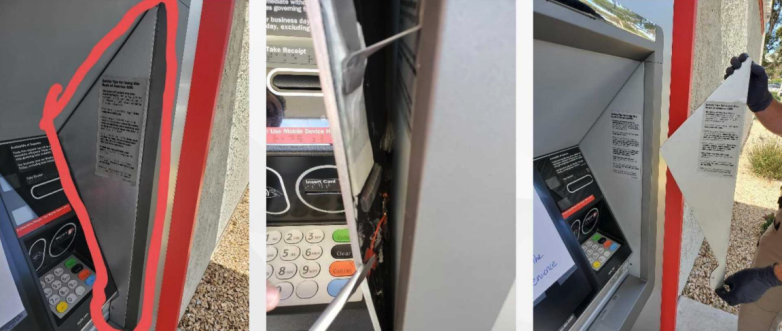
Pinhole spy cameras are sometimes embedded in fake panels above PIN pads by skimmer thieves. As a result of incorporating insert kit into the ATMs of financial institutions, most of the insert skimmer attacks at this point have been successfully stopped.
The insert kit is a solution that NCR has developed to mitigate such attacks. A “smart detect kit” from NCR is also tested in field situations, which includes a USB camera to be able to monitor the interior of the card reader, which adds a photographic element to the test.
There will be a continued trend of miniaturization and stealthy device development for skimming devices as long as cardholder data will continue to be stored on magnetic strips on payment cards in plain text.
Whenever you are at a cash machine, make sure you make your mind up to avoid ATMs that are dodgy-looking or that have a low lighting fixture. And not only that even make sure to cover PIN pad with your hand to defeat such thefts.
Download Free SWG – Secure Web Filtering – E-book







