

When a DDoS attack is conducted, the server being targeted receives a large number of garbage requests. As a result, the server’s capacity is depleted, and a large number of garbage requests are being sent.
As Akamai reported recently, one of the largest DDoS attacks ever launched against a customer in the Asia-Pacific region. This attack has been mitigated by the company after it had launched against that customer.
At its peak, there were 900.1 gigabits per second and 158.2 million packets per second of attack traffic, according to the reports presented by the Akamai.
Record DDoS Attack
The top mitigation on September 12, 2022, was a DDoS attack that targeted a client in Eastern Europe and resulted in the highest mitigation for the company.
This attack resulted in a volume of packets sent per second reaching 704 million, 4.5 times more than the recent event. Unfortunately, we cannot provide volumetric data for this attack at this time because it’s unavailable.
Distributed across scrubbing network
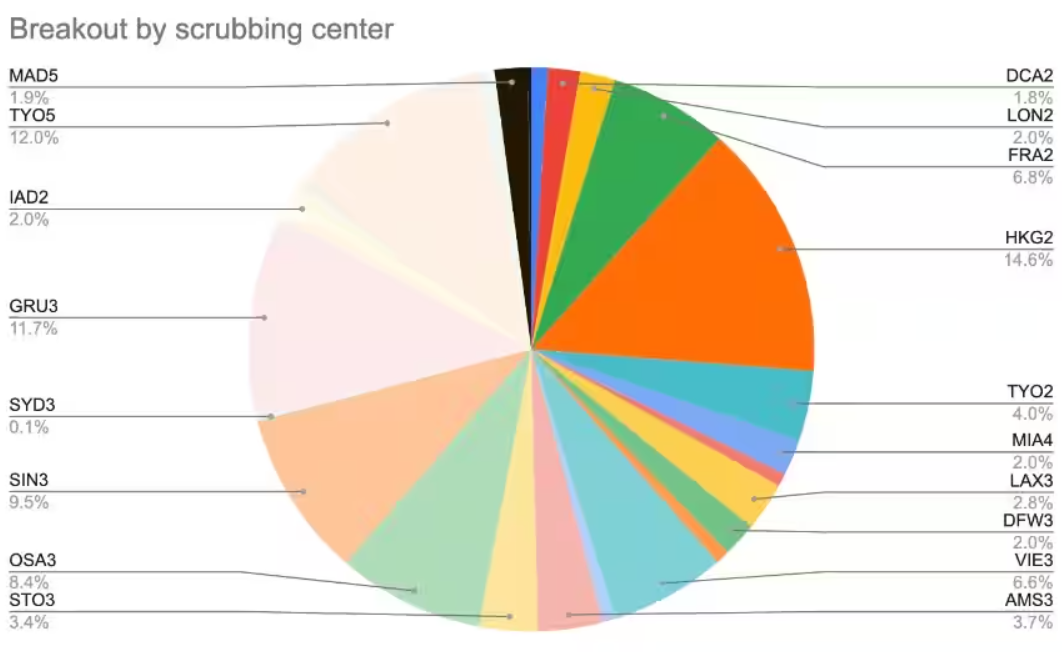
While the attack was distributed across Akamai’s scrubbing network, it primarily originated in APAC, the most heavily targeted region.
The top five scrubbing centers for traffic accounted for less than 12% of the total traffic. However, the top five places are:-
- Hong Kong
- Tokyo
- So Paulo
- Singapore
- Osaka
The experts noticed some amount of attack traffic from all 26 of their scrubbing centers over the last few weeks.
Defense strategy
Using Akamai Prolexic’s industry-leading combination of platform, people, and processes to help thwart this attack and protect our customers, Akamai Prolexic was able to pre-mitigate the attack successfully by implementing the following measures:
- Platform: As such, it is important to have a dedicated defense capability that has the ability to scale up to several times the size of the largest types of attacks that are publicly disclosed.
- People: Six global locations and more than 225 frontline responders with decades of experience mitigating sophisticated attacks for the largest and most demanding organizations in the world.
- Process: Optimize the incident response plans for DDoS attacks after developing custom runbooks, performing service validations, and conducting operational readiness drills.
Recommendations
The Cyber Security and Infrastructure Security Agency (CISA) recommends that you review and implement its recommendations as soon as possible.
- Ensure that there are mitigation controls in place for critical subnets and IP spaces in your network.
- It is always best to deploy DDoS security controls in an always-on mitigation posture to avoid an emergency integration scenario and reduce the burden on incident responders in an attack.
- The situation response plan and runbooks need to be updated on a regular basis to ensure that they are responsive to changes in the situation.
Among the recent cases of this scale is Cloudflare’s mitigation of a DDoS attack that targeted Wynncraft, a Minecraft server that is one of the largest in the world and peaked at 2.5 terabits per second.
Network Security Checklist – Download Free E-Book
Related News:
- Record-Breaking DDoS Attack – Over 71 Million RPS
- Hackers Launched Record DDoS Attack with 25.3 Billion Requests in 4 Hours
- Aggressive DDoS Attack – Over 700 Mpps Attack Traffic to Cripple Target Organization
- Largest DDoS Attack Ever – 659.6 Million Packets Per Second
- 26 Million Request Per Second DDoS Attack Detected – Largest HTTPS DDoS Ever Recorded
- Ransom DDoS Attack that Reached a Rate of 2.5 Million Requests per Second







