Sunday, October 18, 2026

Hackers using Facebook and YouTube Profiles to Host Astaroth Malware C2 Server

Cybercriminals abusing Facebook and YouTube profiles to host the Astaroth malware that launches through sophisticated phishing campaign to target mainly Brazilian citizens.

Threat actors behind the Astaroth Trojan using a various trusted source to compromise and steal the sensitive the data from the victims.

Security research community motioning Astaroth Trojan activities since 2018 and the malware evade the various security protection by abusing the antivirus to intrude the targeted device.

Astaroth leverages the legitimate windows services to drop the payload, and the method will help to easily bypass the security protection.

Researchers from Cofense uncovered a phishing email campaign that temp users to open a .htm file which is the initial stage of start the infection.

Astaroth Malware Infection Process

Once the Victims opens the .htm file, it downloads a zip file that contains .LNK file which downloads JavaScript.

Soon after Javascript code download multiple files that execute the Astaroth information stealer.

Researchers discovered a two .DLL files that associated with the legitimate program ( ‘C:\Program Files\Internet Explorer\ExtExport.exe’.) to run malicious code from trusted sources.

According to Cofense report ” The legitimate programs that were targeted for process hollowing were unins000.exe, svchost.exe, and userinit.exe. The program unins000.exe is most notably used within a security program on systems that allow online banking in Brazil. After the program’s process is hollowed out and replaced with malicious code, Astaroth begins to retrieve the Command and Control (C2) configuration data from outside trusted sources. “

In order to maintain the C2 configuration data, threat actors using the Facebook and YouTube profiles description with base64 encoded and custom encrypted.
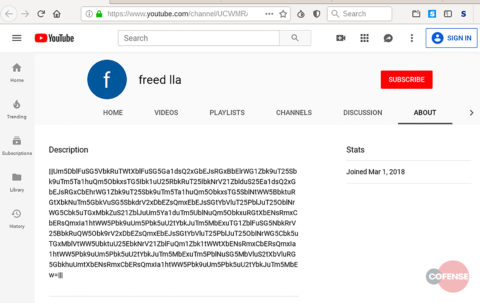
Threat actors cleverly hosting the C2 data within these trusted sources to bypass the network security, and gather the victim’s information to collect the sensitive information such as stored passwords in the browser, email client credentials, SSH credentials, and more.

After the malware collects all the data, it bundles and encrypts sent via HTTPS POST to a site from the C2 list.

Balaji
Balaji
BALAJI is an Ex-Security Researcher (Threat Research Labs) at Comodo Cybersecurity. Editor-in-Chief & Co-Founder - Cyber Security News & GBHackers On Security.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Hackers Use ConnectWise SkyKick Credentials to Access Microsoft 365, Halting Cloud Backups

Attackers abused compromised ConnectWise Cloud Backup credentials to access...

Anthropic’s Claude AI Uncovers Origins of NSA-Provided Cryptographic Keys After 25 Years

Anthropic says an internal Claude research model reconstructed how...

OpenBSD Kernel Flaw Dating Back 37 Years Enables Local Privilege Escalation to Root

A newly disclosed OpenBSD kernel exploitation chain combines a...

GhostAction Hackers Hide Credential-Stealing Malware in Fake Font Files Across 94 GitHub Repositories

GhostAction attackers have expanded their GitHub credential theft campaign...

SideCopy Hackers Target Indian Organizations With ReverseRAT Malware to Steal Data

Indian authorities have warned that SideCopy hackers are targeting...

New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial...

New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six...

Related Articles

Recent News


