

The Javascript-based infection framework for the Gootkit RAT increasingly delivers a wider variety of malware, including ransomware payloads.
The delivery system for the Gootkit information stealer has advanced into a complex and stealthy framework, known as Gootloader, and currently pushing a wider variety of malware via hacked WordPress sites and malicious SEO techniques for Google results.
The Gootkit malware family has been around for more than half a decade, a mature Trojan with functionality centred around banking credential theft.
Experts from Sophos Labs says “In addition to the REvil and Gootkit payloads, Gootloader has been used most recently to deliver the Kronos trojan and Cobalt Strike”.
Gootloader has moved as much of its infection infrastructure to a “fileless” methodology as possible.
Search Engine Deoptimization as a Root Cause
Gootloader uses malicious search engine optimization (SEO) techniques to squirm into Google search results.
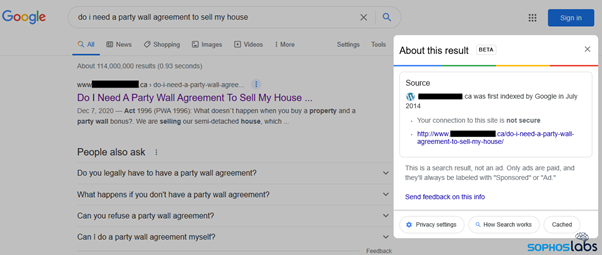
To accomplish this phase of the attack, the operators of Gootloader must maintain a network of servers hosting hacked, legitimate websites.
The screenshot shown above belongs to a legitimate business, a neonatal medical practice based in Canada. None of the site’s legitimate content has anything to do with real estate transactions – its doctors deliver babies – and yet it is the first result to appear in a query about a very narrowly defined type of real estate agreement.
Upon clicking the link in this search result, they’re presented with a specific page that seems to deliver the answer to their exact question, using precisely the same wording as the search query (which sometimes comes across quite awkwardly).


After the visitor clicks the “direct download link”, they receive a .zip archive file (as shown above) with a filename that exactly matches the search query terms used in the initial search. This .js file is the initial infector and the only stage of the infection at which a malicious file is written to the filesystem.
Gootloader Payload Delivery Mechanism
The first-stage script, which is obfuscated, attempts to contact the command-and-control (C2) server – if it successfully does so, the second-stage malware process and creates an autorun entry for a PowerShell script that doesn’t execute until the system reboots, creating a stealthy way for attackers to sidestep detection.
Once the computer reboots, the PowerShell script runs and begins a dominoes-like sequence of events, ending with Gootloader attempting to download its final payload.
“The Delphi loader contains the final payload – Kronos, REvil, Gootkit, or Cobalt Strike – in encrypted form,” said researchers. “In those cases, the loader decrypts the payload, then uses its own PE loader to execute the payload in memory.”
Final Word
Script blockers like NoScript for Firefox could help a cautious web surfer remain safe by preventing the initial replacement of the hacked web page to happen. Even attentive users who are aware of the trick involving the fake forum page might not recognize it until it’s too late.
In the end, it’s up to the search engines, whose algorithm the malware games to get a high search result, to address the initial attack vector.
“Users can be trained to do things like enabling visible file suffixes in Windows, so they can see they’re clicking a file with a .js extension, but they can’t choose which search results appear near the top of the list or how those sites get manipulated by threat actors”, said researchers.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity, and hacking news updates.







