
A campaign that began late last year targeting eight different Malaysian banks is still targeting its customers with three malicious Android applications.
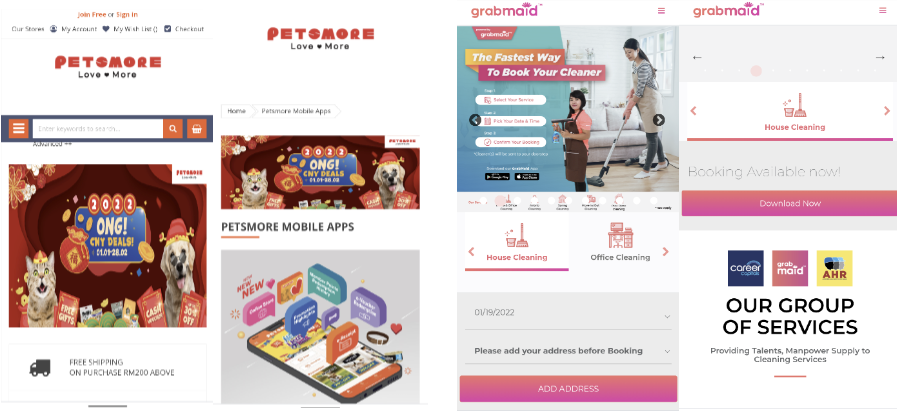
Under the guise of seemingly harmless shopping apps, the threat actors in this campaign have misled users into installing malicious applications. As a way to get people to download the applications, some of the websites copy the original to the point of outright copying.
The security experts at Slovak cybersecurity firm ESET stated:-
“In these attacks or campaigns, malicious websites were set up by the attackers to trick users into downloading the malicious apps by appearing as legitimate, but fraudulent, websites.”
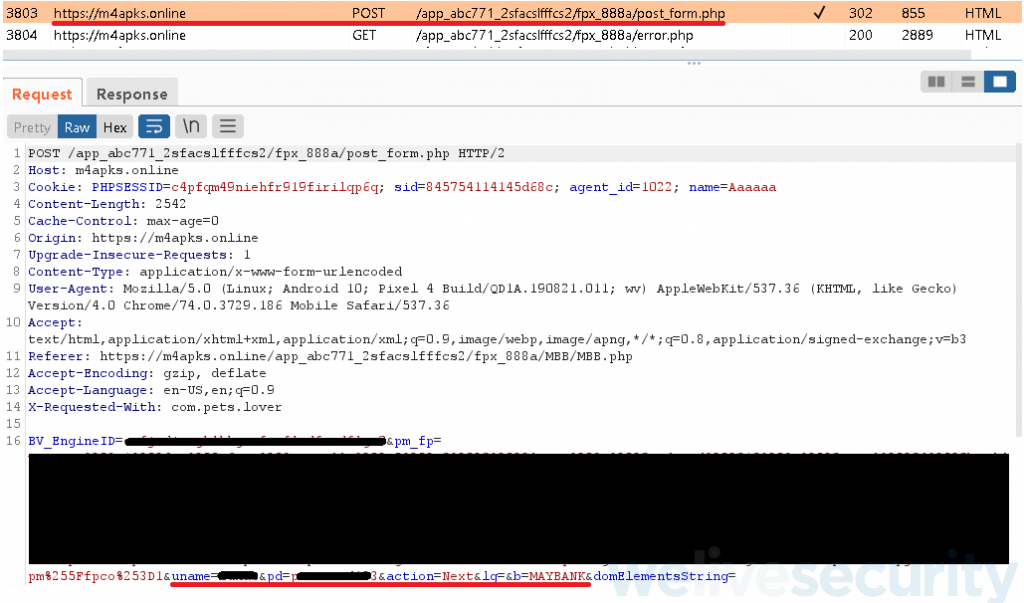
In addition to stealing credentials, the apps allow attackers to forward all SMS messages from the victim that include 2FA codes sent by their banks to the malware operators.
Banks & Websites Targeted
In total, the threat actors have targeted 8 Malaysian banks, and here we have mentioned them all:-
- Maybank
- Affin Bank
- Public Bank Berhad
- CIMB bank
- BSN
- RHB
- Bank Islam Malaysia
- Hong Leong Bank
Here the threat actors have copied the websites of the cleaning services and a pet store:-
- Grabmaid
- Maria’s Cleaning
- Maid4u
- YourMaid
- Maideasy
- MaidACall
- PetsMore
Campaign and Goal
In this latest campaign, all the websites are seen using domain names whose domain names are similar to those of the services that they pretend to represent.
Along with the security analysts at ESET, the MalwareHunterTeam has claimed:-
“Facebook ads are also used by the attackers to distribute the fake websites they have created. As a result, it was also discovered that there are three other malicious websites and Android trojans associated with the campaign.”
The attack depends on the potential victim enabling the non-default “Install unknown apps” option on their device for it to succeed. Because of this, five of the services that are abused don’t even have a Google Play app, which makes matters worse.
As soon as the app is launched, the user will be prompted to sign in. Doing so will allow them to place false orders and then they will be presented with different options to accept payments from their bank accounts in order to complete the checkout process.
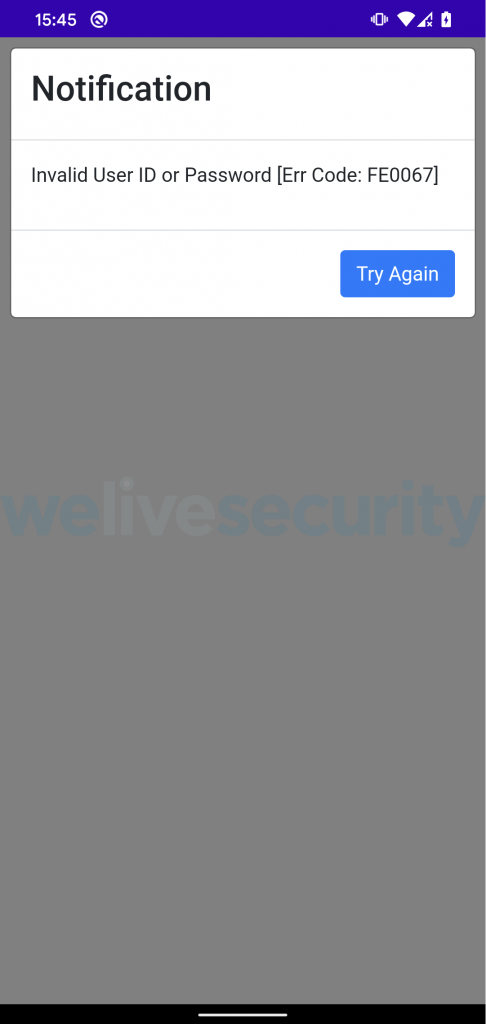
Campaigns such as this are mainly designed to obtain users’ banking credentials and exfiltrate them to a server that is controlled by the attacker. During this process, they will display an error message about an invalid user ID or password entered.
Moreover, the ESET malware researcher, Lukáš Štefanko stated:-
“While the campaign targets Malaysia exclusively, for now, it might expand to other countries and banks later on. At this time, the attackers are after banking credentials, but they may also enable the theft of credit card information in the future.”
Mitigations
Here below we have mentioned all the recommended mitigations:-
- Always verify if the website is secure or not.
- Do not follow paid search engine results.
- Beware of clicking suspicious ads.
- Don’t download any app from unknown sources.
- Always try to use software or hardware-based 2FA mechanism.
- Always use robust mobile security solutions.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.






