

The threat actor gained attention in February 2025 after successfully hijacking a subdomain of the U.S. Centers for Disease Control and Prevention (CDC).
Sophisticated threat actor dubbed “Hazy Hawk” has been exploiting DNS misconfigurations since at least December 2023 to hijack abandoned cloud resources from high-profile organizations, according to new research.
The threat actor utilizes these hijacked subdomains to distribute scams and malware, leveraging the inherent trustworthiness of the compromised domains to evade security controls and achieve higher rankings in search results.
Investigators discovered hundreds of malicious URLs suddenly appearing on the CDC subdomain which resolved to an abandoned Azure website resource.
Further investigation revealed a much broader campaign targeting dozens of major organizations worldwide, including federal government entities (alabama.gov, health.gov.au), universities (berkeley.edu, ucl.ac.uk), healthcare organizations, and major corporations like Deloitte, EY, PwC, and TED.
Hazy Hawk specifically targets cloud resources across multiple providers including Akamai, Amazon (EC2, S3, Elastic Beanstalk), Azure, Bunny CDN, Cloudflare CDN, GitHub, and Netlify.
The discovery of vulnerable DNS records is a complex problem and indicates that Hazy Hawk has access to a large passive DNS service.
Security researchers note that the discovery of these vulnerable DNS records indicates the actor has sophisticated capabilities and likely access to commercial passive DNS services.
Advanced Threat Actor
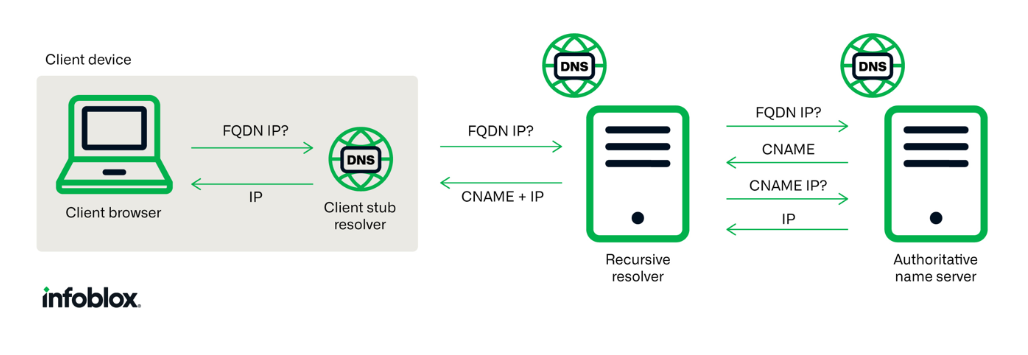
The attacks exploit CNAME records – DNS entries that map one domain name (alias) to another.
When organizations abandon cloud resources but fail to remove associated DNS records, these “dangling” CNAME records become vulnerable to hijacking.
Unlike traditional domain hijacks targeting unregistered domains, Hazy Hawk’s methodology requires significant technical sophistication.
The threat actor identifies these misconfigurations, registers the missing resources, and uses them to host malicious content.
Unlike traditional domain hijacks targeting unregistered domains, Hazy Hawk’s methodology requires significant technical sophistication.
Cloud resource hijacking is significantly more challenging because each provider handles missing resources differently, and some, like Azure, have implemented specific preventative mechanisms.
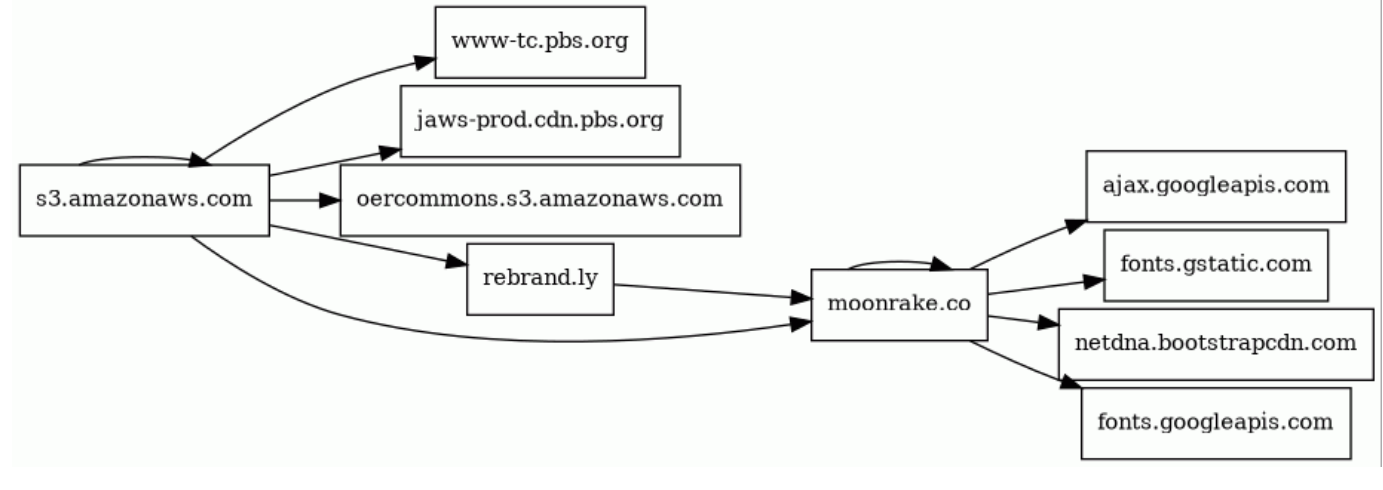
The threat actor employs sophisticated obfuscation techniques, including URL redirection, AWS S3 bucket obfuscation, and content cloning from legitimate websites like PBS.org.
Malware Distribution Chain Delivers Scams
Hazy Hawk creates numerous URLs on hijacked domains that lead victims through a complex chain, ultimately delivering various scams and malware through traffic distribution systems (TDS).
The URLs often redirect through actor-controlled domains on platforms like Blogspot before entering the TDS.
A particularly concerning aspect is the use of push notification requests. Victims who accept these notifications receive persistent browser messages leading to tech support scams, fake antivirus offers, and other fraudulent content.
The FBI reports that such scams caused over $3.4 billion in losses among elderly Americans in 2023 alone.
Security experts recommend establishing processes that trigger notifications to remove DNS CNAME records whenever resources are shut down, implementing protective DNS solutions designed to detect TDS actors, and educating users to deny notification requests from unfamiliar websites.
Hazy Hawk exploits organizations’ DNS gaps to abuse cloud resources & deliver malware.
Organizations are advised to implement rigorous DNS management practices, especially when decommissioning cloud resources.
Find this News Interesting! Follow us on Google News, LinkedIn, & X to Get Instant Updates!


