A newly disclosed flaw in ProFTPD is drawing urgent attention because it can let attackers move from a simple SQL injection bug to authentication bypass, privilege escalation, and in some environments even remote code execution.
Tracked as CVE-2026-42167, the issue was found in ProFTPD’s mod_sql extension by ZeroPath Research, and MITRE assigned it a CVSS v3 score of 8.1, placing it in the high-severity range.
The risk is especially serious for internet-facing FTP servers that use SQL-backed logging or authentication, because the attack can be triggered remotely and may not always require a valid login first.
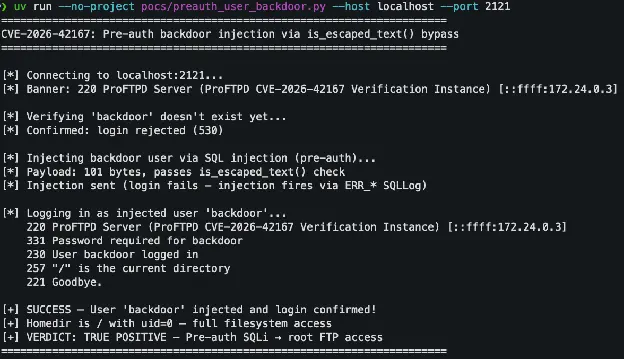
At the core of the bug is the way mod_sql handles data that appears to be already escaped before adding it into SQL queries.
According to public analysis, attacker-controlled values such as usernames can be passed into logging expressions like %U, and the vulnerable logic may treat crafted input as safe even when it is actually malicious SQL.
That means a specially formed username or other request field can break out of the intended query structure and inject database commands of the attacker’s choice.
The impact depends heavily on how the administrator has configured ProFTPD.
If mod_sql logging is enabled for pre-authentication commands such as USER, and those log formats include attacker-controlled data, a remote attacker may be able to exploit the flaw before logging in at all.
In other setups, the attacker may need a valid account or anonymous FTP access first. However, even then, the injected SQL can still be used to create backdoor users, alter privileges, or read sensitive data from the backend database.
The worst-case scenario appears when ProFTPD is connected to PostgreSQL with powerful privileges.
In that configuration, SQL injection can be chained to operating system command execution by abusing database features that allow commands to run from SQL, which is why the flaw is described as an RCE risk rather than a simple data exposure bug.
Even where direct code execution is not possible, researchers say the same weakness can still be used to bypass authentication, steal credentials, and abuse privileges, making it a broad compromise path for affected servers.
ZeroPath says the bug affects ProFTPD versions up to 1.3.9 and that the vendor addressed it in ProFTPD 1.3.9a, released on April 27, 2026, after coordinated verification work and CVE assignment earlier in the month.
The official CVE record also describes vulnerable ProFTPD releases as builds before 1.3.10rc1, showing that defenders should rely on patched vendor packages rather than assume an older branch is safe by default.
Administrators should upgrade immediately, review whether mod_sql is enabled, and check the SQLNamedQuery and SQLLog directives for any use of attacker-controlled fields in SQL statements.
If patching cannot happen right away, the safest temporary step is to turn off mod_sql-based logging, monitor authentication attempts and database activity for unusual behavior, and treat exposed ProFTPD servers as high priority until the fix is applied.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.