

The cybersecurity analysts at ASEC security firm have recently identified a new malware that is dubbed as PseudoManuscrypt on numerous Windows systems that are located in South Korea.
While this new PseudoManuscrypt malware was operating the same delivery tactics of another malware, CryptBot since May 2021. Not only this, even PseudoManuscrypt is primarily disseminated through malicious websites that are easily accessible on the top search pages of several search engines.
Here’s what the experts of ASEC security firm have stated:-
“PseudoManuscrypt is disguised as an installer that is similar to a form of Cryptbot and is being distributed. Not only is its file form similar to Cryptbot, but it is also circulated via malicious sites exposed on the top search page when users search commercial software-related illegal programs such as Crack and Keygen.”
PseudoManuscrypt’s spread
In South Korea, this new malware, PseudoManuscrypt infects over 30 computers on an average daily basis, and this malware was initially tracked by Kaspersky in December 2021.
At the time of its initial discovery, the Kaspersky security firm has revealed key data and fragments of a mass-scale spyware attack campaign, and in this malicious campaign, it has compromised more than 35,000 systems in 195 countries around the world.
And here below we have mentioned the operation flow of PseudoManuscrypt malware:-
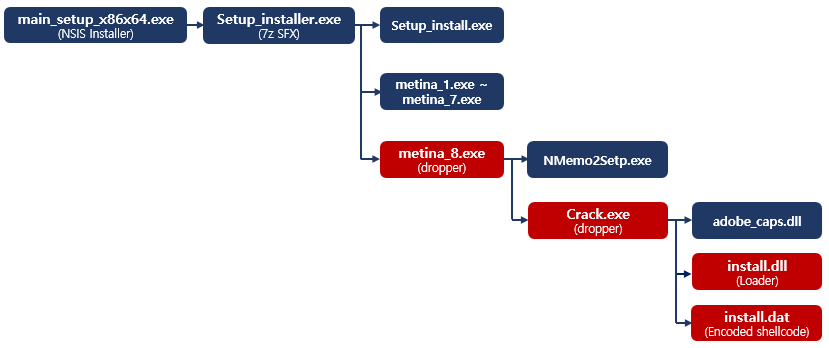
With a full-featured payload module, the threat actors behind this malware can take full control of the compromised systems with several spying abilities.
Types of data compromised
Here below we have mentioned all the types of data compromised by the threat actors by deploying this malware on the targeted systems:-
- VPN connection information
- Clipboard data
- Audio data
- List of shared network folders
- Information of processes that accept TCP and UDP ports
- File version information of the running process
- C2 : email.yg9[.]me
- File download
- Execute arbitrary commands
- Log keypresses
- Capture screenshots
- Videos of the screen
Targets of PseudoManuscrypt
In June 2021, the targets of PseudoManuscrypt malware was originally disclosed and it includes the following organizations and companies from Russia, India, and Brazil:-
- Industrial organizations
- Government organizations
- Private enterprises
- Enterprises military-industrial complex
- Research laboratories
Moreover, all the malicious files that are downloaded by the PseudoManuscrypt malware can be enlisted to offer services and perform constant malicious activities by mimicking them as periodic PC maintenance to deceive the users.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.






