

AhnLab Security Emergency Response Center (ASEC) has recently revealed a disturbing case of Remcos RAT, a malicious software that can remotely access and manipulate infected machines.
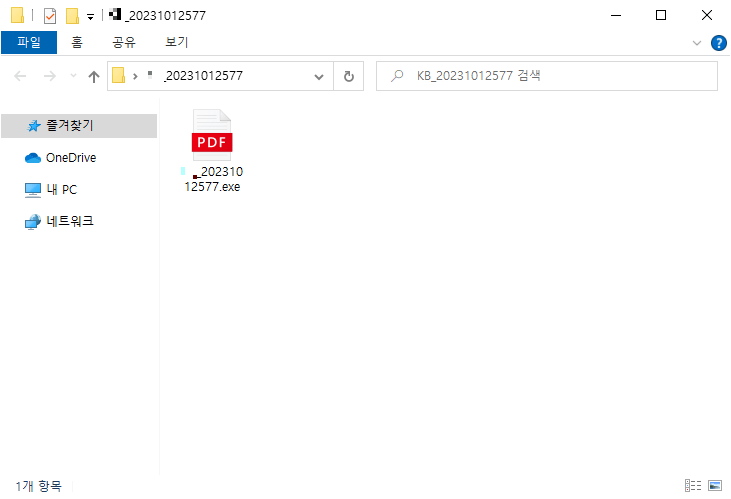
The attackers behind this malware used a clever email scam that pretended to be a payslip to trick the recipients into opening a compressed CAB file that contained the Remcos RAT disguised as a PDF file.
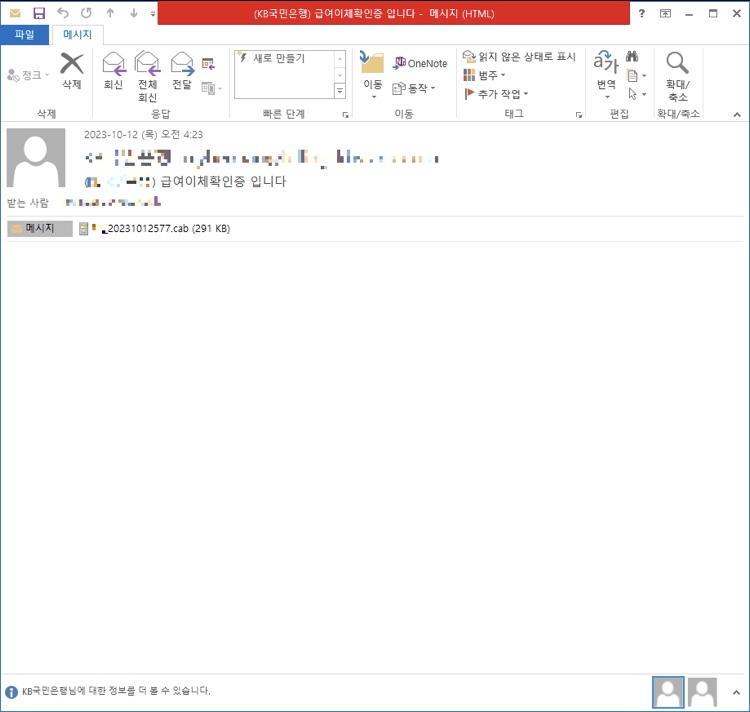
This sneaky trick allowed the Remcos RAT to enter the target’s system, giving the attacker a lot of malicious options.
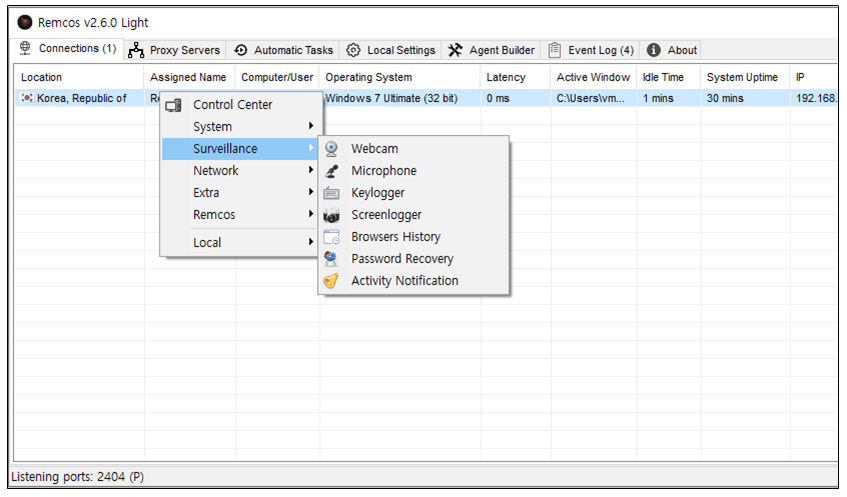
The Remcos RAT, once run, has many intrusive capabilities. It can log keystrokes, take screenshots, control webcams and microphones, and execute various actions as per the attacker’s commands.
It can also steal sensitive data, such as browsing histories and stored passwords, from the victim’s system.
Interestingly, the Remcos RAT stays inactive until it gets commands from the attacker’s command and control (C2) server.
This helps it evade detection by security systems. However, it has a unique feature that makes it different from typical remote-access trojans.
The Remcos RAT has an offline keylogger that starts working right after infection without needing a command from the C2 server.
This creates a weakness that can be used for detection, especially with sandbox devices.
Various control features of the Remcos RAT’s remote control server (Remcos v2.6.0
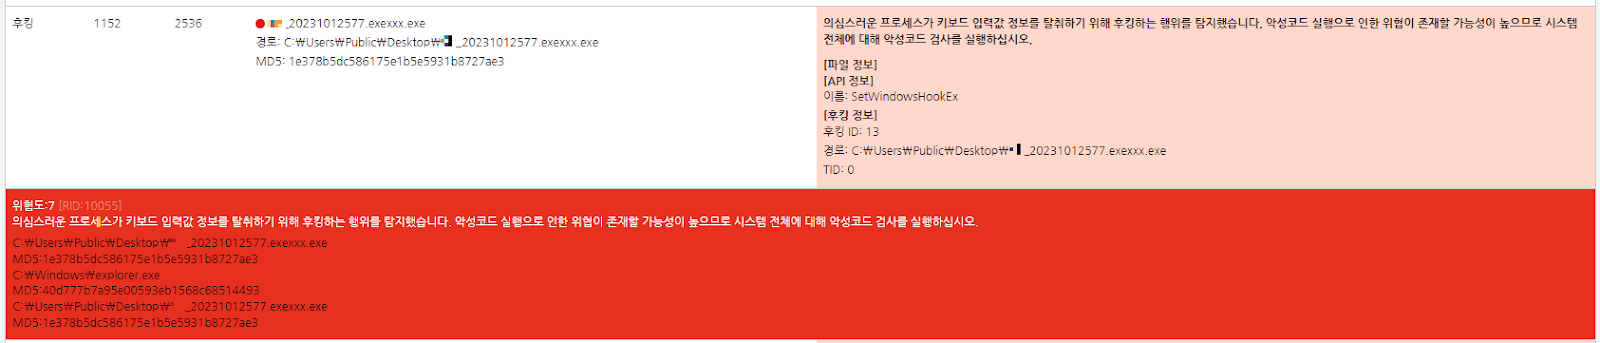
The offline keylogger in the Remcos RAT works by using the SetWindowHookExA API and installing a hook procedure to monitor keyboard input events through the WH_KEYBOARD_LL argument.
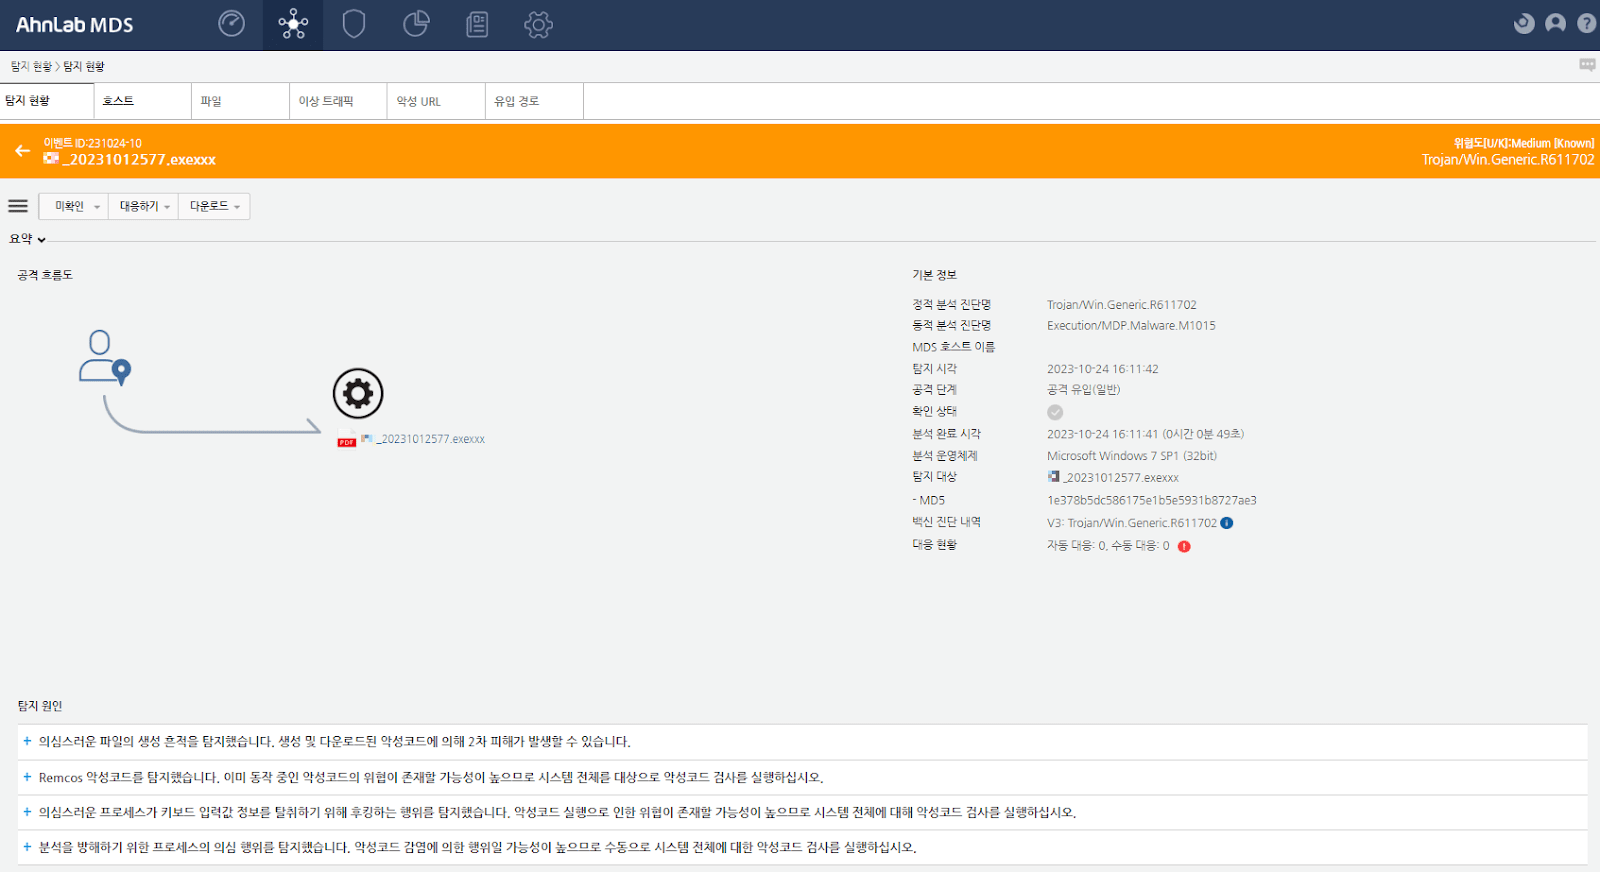
AhnLab’s MDS sandbox environment successfully detects the malicious behavior of this offline keylogger.
This feature helps to identify the Remcos RAT’s presence even before it connects with the C2 server.
Remcos RAT malware detected using AhnLab MDS (2)
To conclude, Remcos RAT is a serious threat that can do a lot of harm. Its unique offline keylogger feature offers a chance for detection, making it important for security administrators to use advanced threat prevention solutions, such as MDS, and to carefully monitor endpoint environments for any unusual behaviors using products like EDR.
Protect yourself from vulnerabilities using Patch Manager Plus to patch over 850 third-party applications quickly. Try a free trial to ensure 100% security.


 has recently revealed a disturbing case of Remcos RAT, a malicious software remotely access.)