

Following its attack against users in the following countries, the Roaming Mantis operation has now attack users in France with Android and iOS devices.
- Germany
- Taiwan
- South Korea
- Japan
- The US
- The UK
Around tens of thousands of users per day, Roaming Mantis has been targeting a variety of European users as early as February. As a result of the threat actor’s motivations, it has been speculated that they are financially motivated.
In a phishing SMS, an analyst at SEKOIA.IO was sent with a malicious URL embedded in it. As a consequence of clicking on this URL, the MoqHao (XLoader) Android malware is either deployed or a page is redirected that allows credential collection from Apple login details.
There is a possibility that some 70.000 Android devices have been compromised during this campaign which impacts France widely.
Roaming Mantis Drops XLoader
A new payload, XLoader (MoqHao), is being dropped on Android devices by the Roaming Mantis group. This malware is counted as one of the most powerful malware since it has several interesting features like accessing the host remotely, stealing information, and spam SMS messages from the victim’s phone or computer.
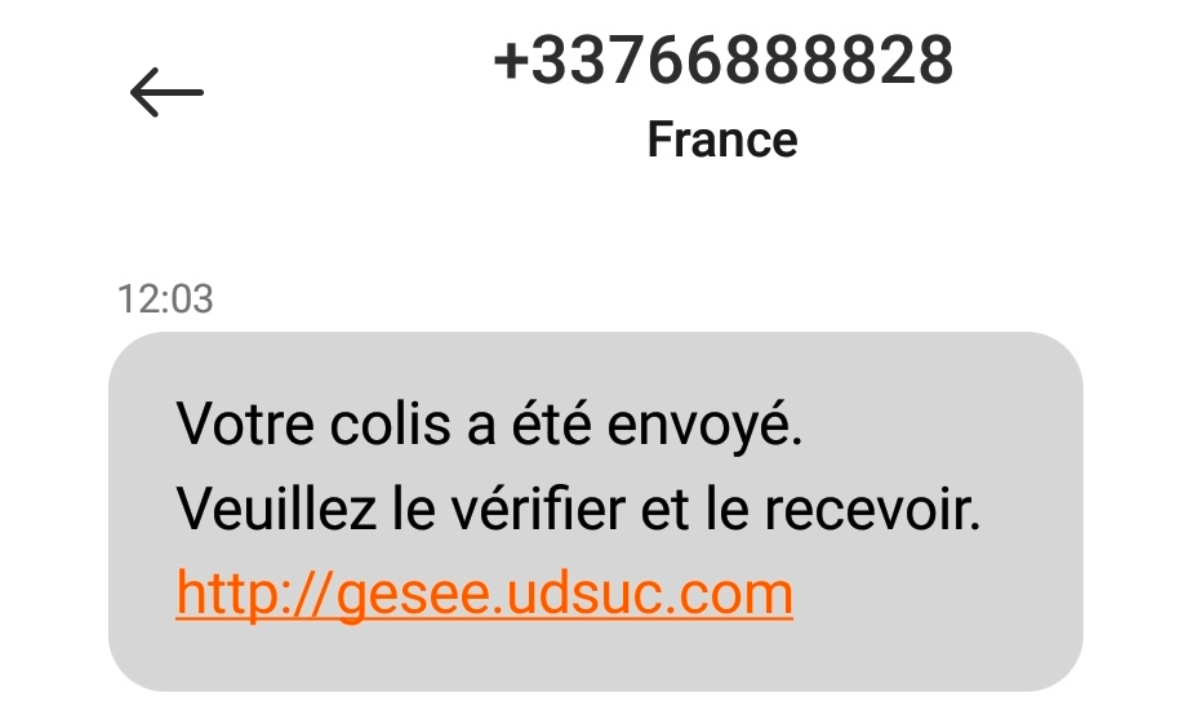
French users are the target of the Roaming Mantis campaign that is currently ongoing. As soon as the attack is initiated, victims are sent a text message with a URL that entails them following a specific link.
They are being informed to review and arrange the delivery of a package they have received through a text message.
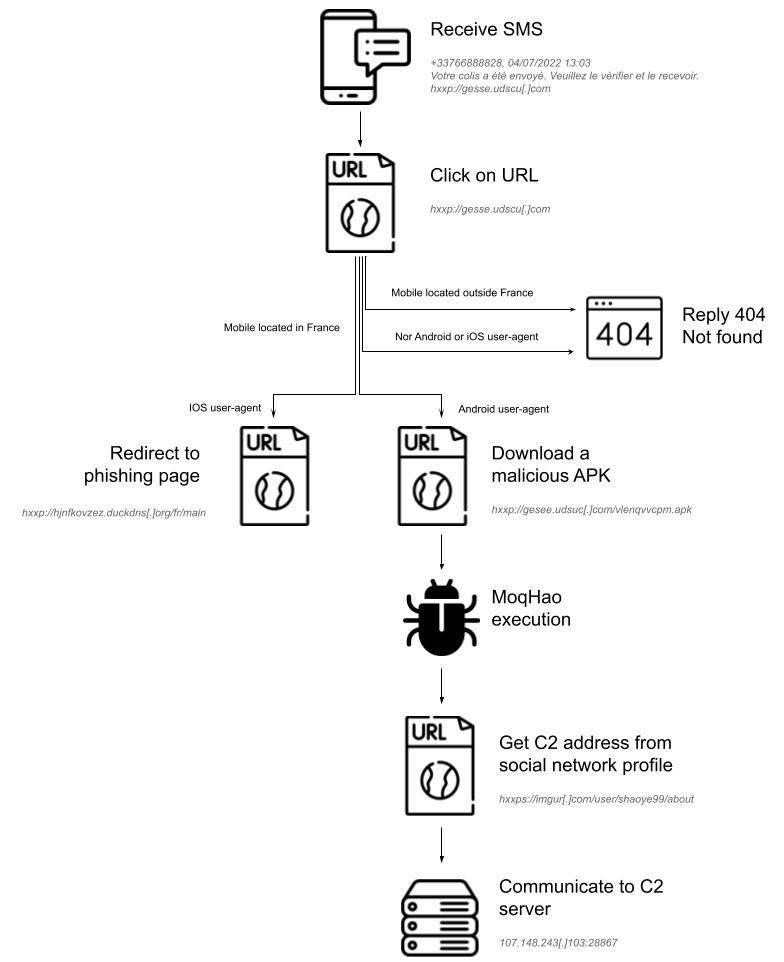
The user is directed to a phishing page, which steals Apple credentials from the user if they are based in France and using an iOS device.
The Android user is redirected to a website that contains the installation file for a mobile app that is available for download.
Getting a 404 error from Roaming Mantis’ servers is an indication that the attack has ended for customers outside France.
Permissions Requested & Exploited
The APK is a malicious application that replicates the Chrome installation and requests unauthorized access to sensitive data and permissions like:-
- SMS interception
- Making phone calls
- Reading storage
- Writing storage
- Handling system notifications
- Access to accounts list
Several hard-coded Imgur profile destinations are used to retrieve configuration information for C2 which is encoded in base64 in order to make it more difficult to detect.
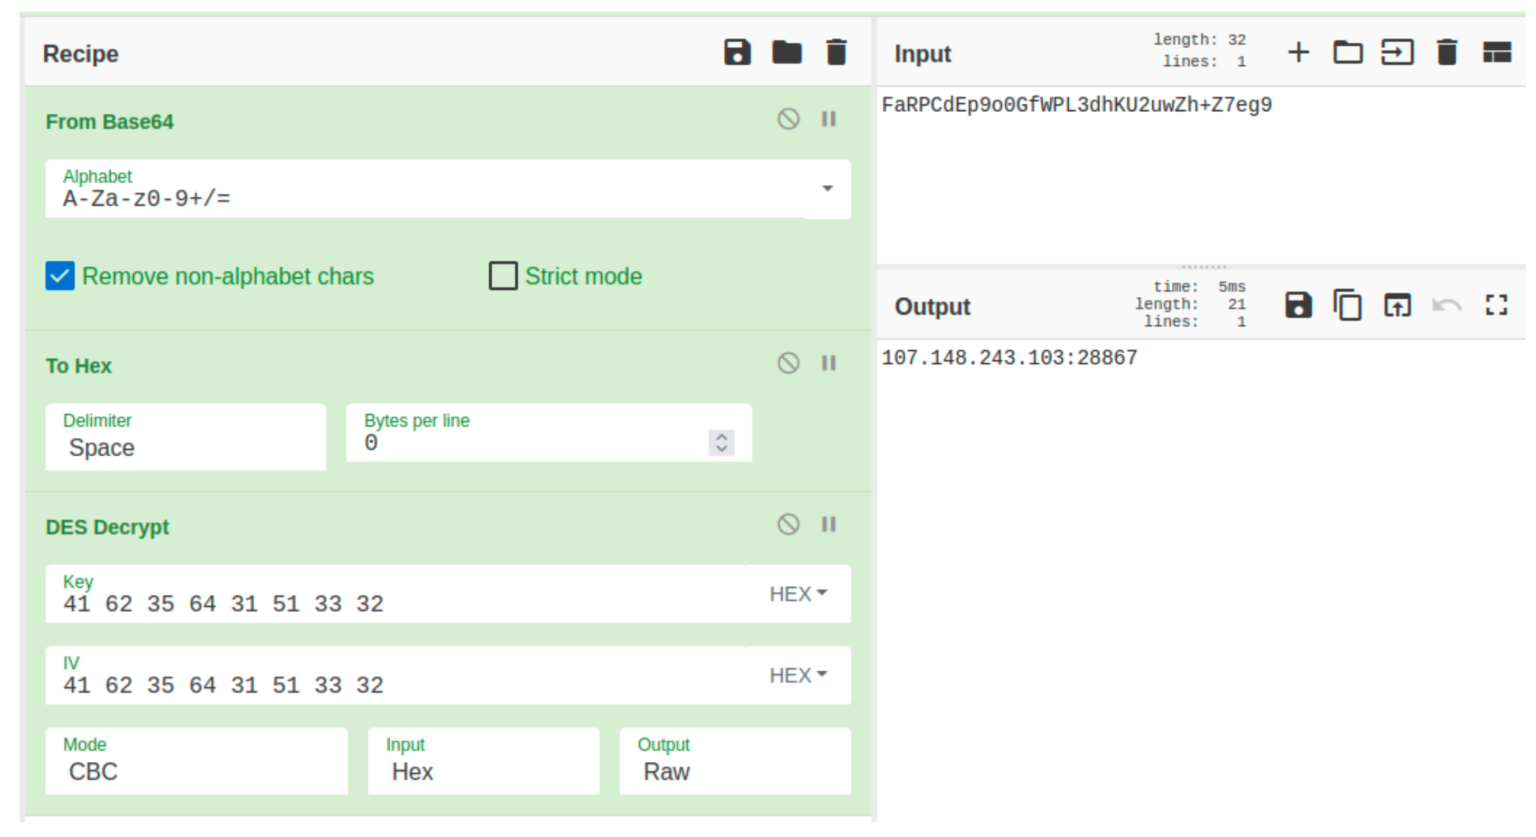
Moreover, XLoader has been requested from the main C2 server by more than 90,000 unique IP addresses. Since the last time Roaming Mantis was analyzed, few changes have been made to its infrastructure.
There are still open ports on the servers at the following addresses:-
- TCP/443
- TCP/5985
- TCP/10081
- TCP/47001
In spite of the fact that the same certificates have been in use since April. Over 100 subdomains are used in the intrusion set, and dozens of FQDNs are used to resolve each IP address that is associated with it.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







