
New tactics used by threat actors who embed phone numbers in scam emails as a key indicator of compromise (IOC), revealing how attackers exploit VoIP infrastructure to evade detection and scale fraud operations.
Telephone-oriented attack delivery (TOAD) remains a dominant phishing technique, in which victims are lured to call attacker-controlled numbers rather than clicking malicious links.
This shift allows scammers to manipulate targets in real time, often leading to credential theft or malware installation.
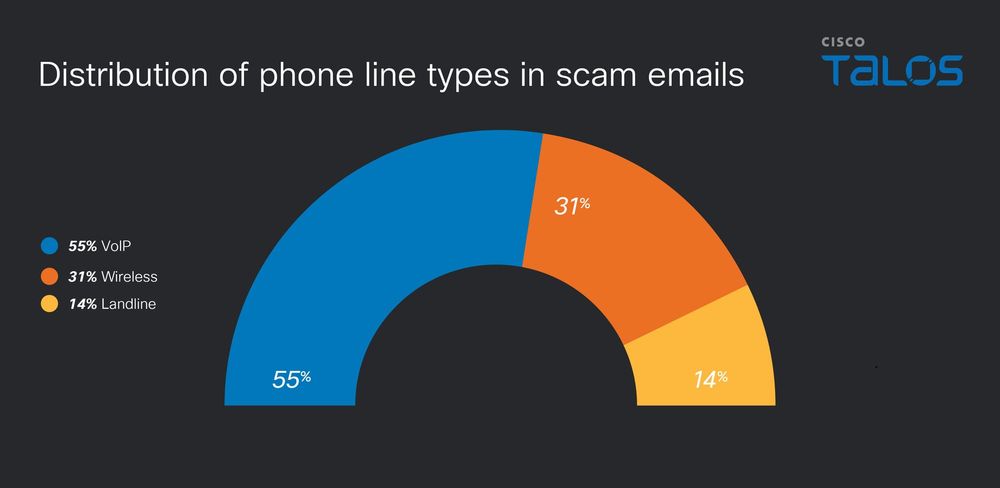
Talos found that Voice over Internet Protocol (VoIP) services are heavily abused due to their low cost, automation capabilities, and ease of provisioning via APIs.
Attackers can rapidly generate large volumes of phone numbers, making attribution and blocking more difficult. During a study conducted between February 26 and March 31, 2026, six out of the ten largest scam campaigns relied on VoIP infrastructure.
VoIP providers fall into two categories: wholesalers and retailers. Wholesalers such as Twilio and Bandwidth supply bulk numbers to smaller providers, while retailers like RingCentral offer end-user communication services.
Cisco Talos has recently started to collect and gather intelligence around phone numbers within emails as an additional indicator of compromise (IOC).
Every number is globally unique and can be routed correctly across the Public Switched Telephone Network (PSTN).
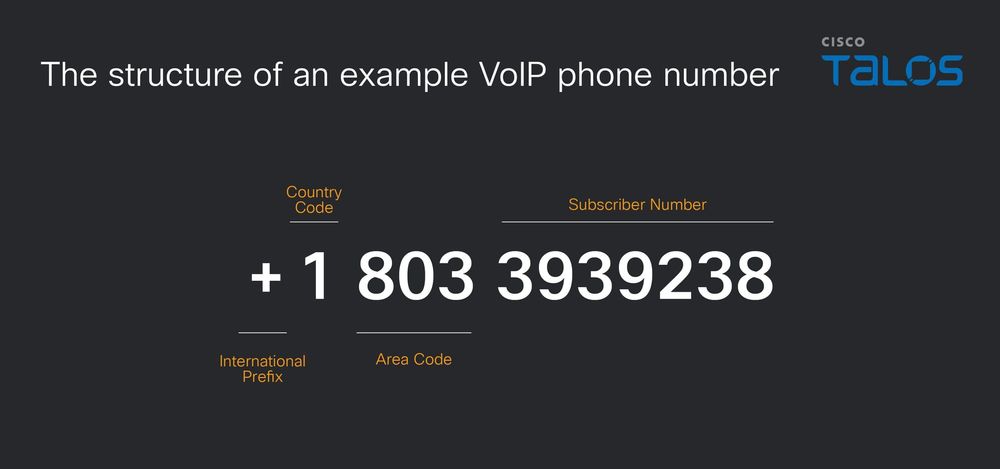
Among these, Communications Platform-as-a-Service (CPaaS) providers are the most exploited, as they enable automated number provisioning at scale. Talos identified Sinch as the most frequently abused provider in observed campaigns.
Scammers Exploit Disposable VoIP
One of the most effective evasion strategies involves limiting the lifespan of phone numbers while reusing them strategically.
Talos identified 1,652 unique phone numbers across major scam campaigns impersonating brands like PayPal, Geek Squad, McAfee, and Norton LifeLock.
Only a small portion about 3.4% were reused across consecutive days, typically for two days, with a maximum observed reuse of four days.
However, attackers also implement “cool-down” periods, temporarily retiring numbers before reintroducing them to bypass reputation-based filters.
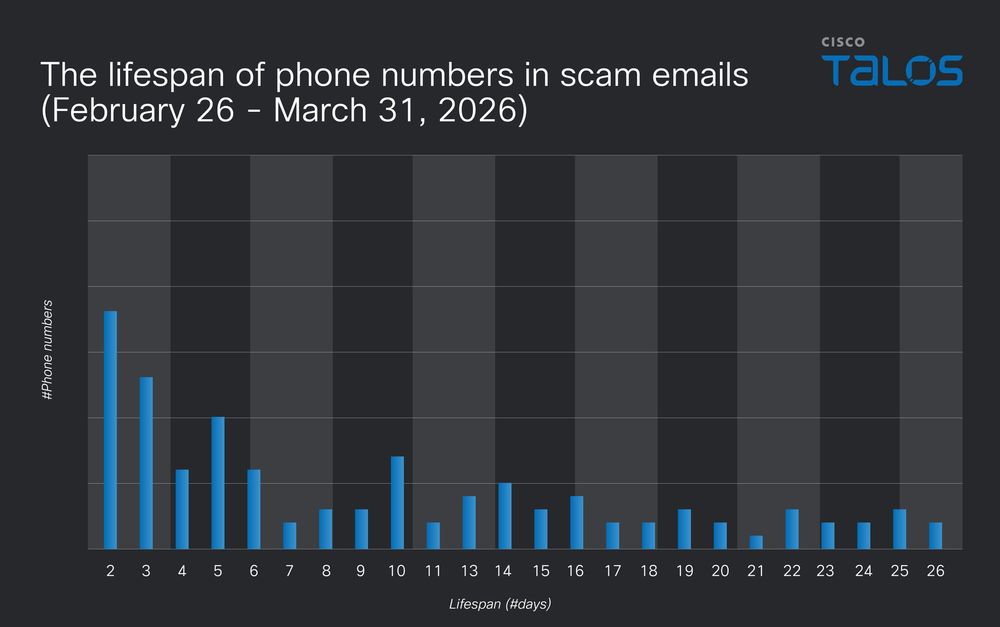
The median lifespan of a scam-related phone number was approximately 14 days, with most active between two and six days. This short lifecycle helps attackers stay ahead of blocklists, which often lag behind rapidly changing infrastructure.
Talos observed that threat actors maximize efficiency by reusing the same phone numbers across different scam scenarios.
A single number may appear in emails with varying subject lines, such as billing alerts, refund notices, or account verification messages.
In more advanced campaigns, the same number was embedded in different attachment types, including PDFs and HEIC image files, to evade traditional detection systems.
Some campaigns even reused a single number while impersonating multiple brands, redirecting victims to the same call center regardless of the lure.
For example, a scammer might send one email posing as PayPal with a “transaction alert” and another as Norton LifeLock with a “subscription renewal,” both directing victims to the same phone number.
Attackers also exploit Direct Inward Dialing (DID) blocks, acquiring sequential ranges of phone numbers. When one number is flagged, they rotate to the next in the sequence.
Talos observed cases where nearly identical numbers differing only in the last digits were used across large-scale campaigns.
The use of HEIC (High Efficiency Image Container) a format often used for iPhone/iPad photos demonstrates the attackers’ efforts to bypass traditional file-based detection while maintaining high image quality.
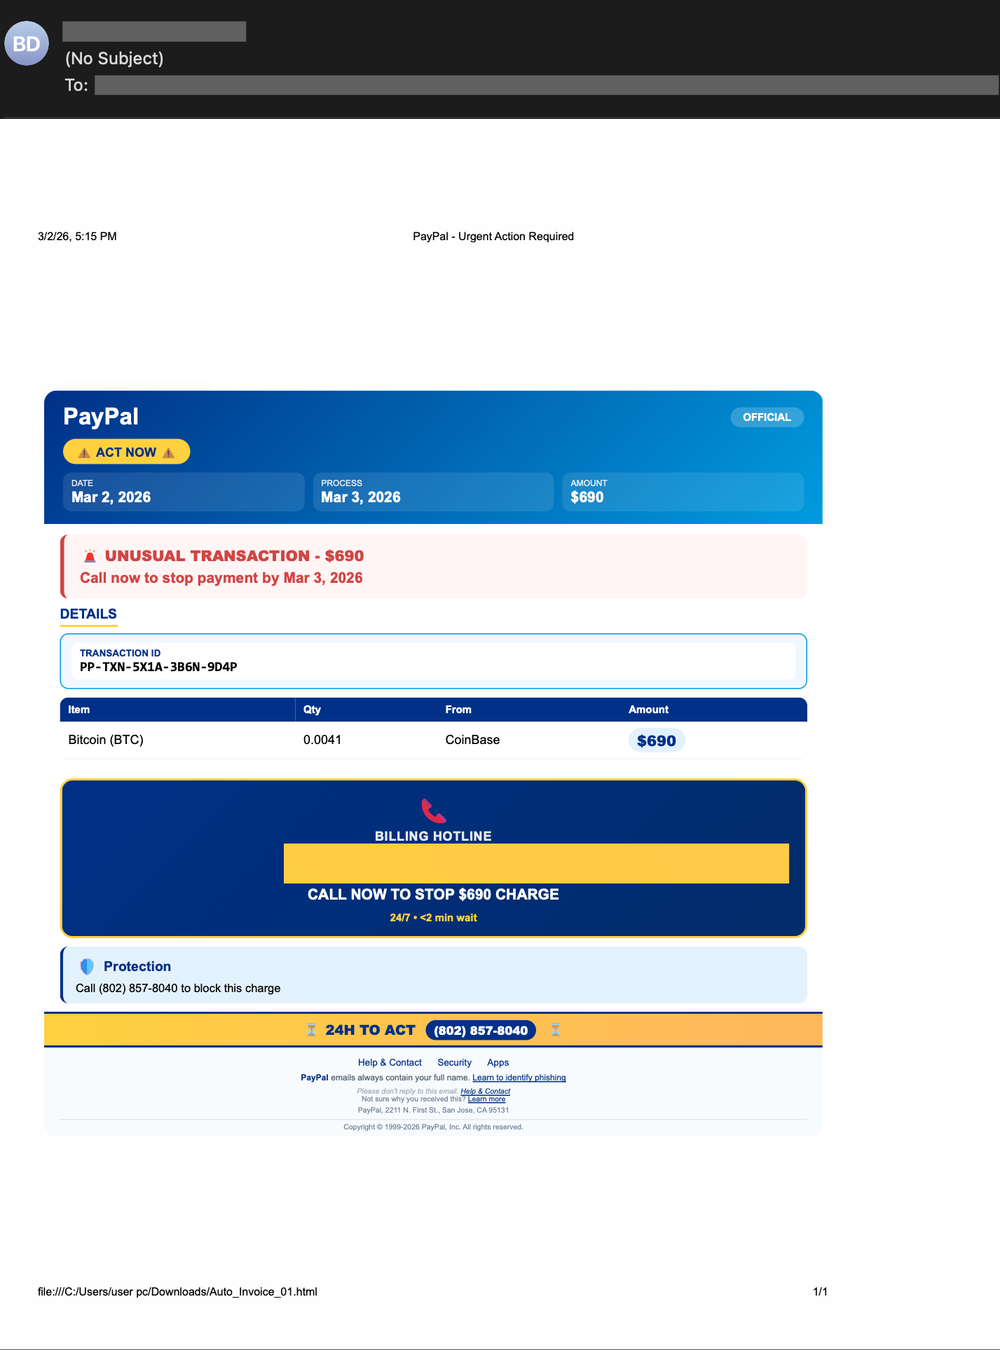
By clustering these numbers, researchers can uncover hidden relationships between seemingly unrelated attacks. This approach shifts the focus from disposable email addresses to more stable infrastructure elements like phone numbers.
Talos emphasizes that tracking phone numbers as IOCs provides a more reliable way to identify and disrupt scam operations.
Security teams are encouraged to adopt real-time reputation systems that include telephony data alongside traditional indicators like URLs and file hashes.
Improved collaboration between VoIP providers and telecom operators is also critical. Sharing intelligence on malicious number usage can help detect patterns earlier and reduce the effectiveness of large-scale scam campaigns.
As attackers continue to evolve their techniques, focusing on phone-based infrastructure offers defenders a valuable opportunity to expose and dismantle organized scam networks.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


, revealing how attackers exploit VoIP infrastructure.)