

The notorious Scattered Lapsus$ Hunters collective has re-emerged from a period of operational dormancy with an escalated recruitment campaign and the development of a new Ransomware-as-a-Service platform.
Recent monitoring of underground Telegram channels and credential-trading forums confirms the group has rebuilt its operational infrastructure and is actively pursuing high-value initial access opportunities across telecommunications, cloud providers, and enterprise software environments.
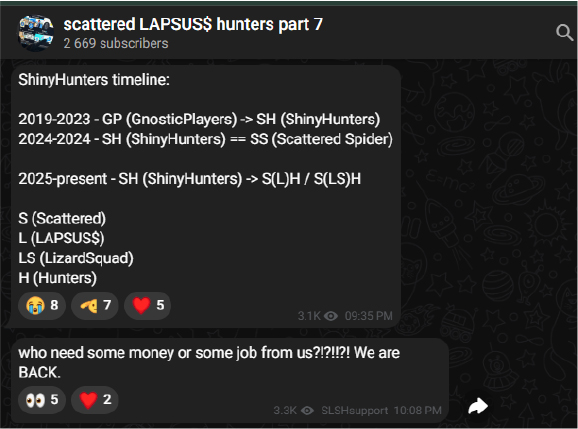
Intelligence gathered from closed chatroom discussions reveals the collective frequently references LizardSquad, though this association remains unverified and appears to be part of a reputation-inflation strategy rather than evidence of a genuine operational partnership.
The group’s reorganization demonstrates a shift toward specialized roles, including social-engineering operators, intrusion specialists, credential brokers, and insider-recruitment facilitators.
Structured Initial Access Acquisition
The collective has published explicit acquisition criteria for initial access purchases, targeting organizations with annual revenues exceeding $500 million while excluding entities in Russia, China, North Korea, Belarus, and the healthcare sector.
Chatroom discussions contain references to the LizardSquad name, although these appear unverified and likely intended to strengthen their perceived threat posture rather than confirm a real partnership.
The group operates a tiered commission structure offering 25 percent payouts for Active Directory-joined systems and 10 percent for Okta, Azure Portal, or AWS IAM root credentials.
Insider recruitment efforts specifically seek operatives capable of providing VPN, VDI, Citrix, or AnyDesk access from telecommunications providers, software and gaming corporations, and business process management environments.
The collective has directly addressed potential insider fears by referencing a recent CrowdStrike insider detection incident, framing it as a self-inflicted disclosure to reassure prospective collaborators about operational security.
In the early days of their resurgence, the group shared a CrowdStrike internal dashboard and an Okta SSO page leaked to them by an employee.
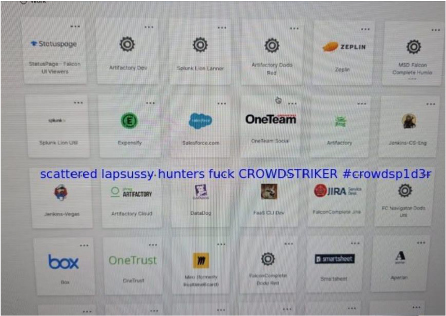
Evidence of the group’s privileged access capabilities surfaced when operators shared screenshots of a CrowdStrike internal dashboard and Okta single sign-on page obtained through an insider collaborator during the early phase of their resurgence.
ShinySp1d3r RaaS Platform
The collective has announced development of ShinySp1d3r, a Ransomware-as-a-Service platform described as a collaboration involving members from ShinyHunters, Scattered Spider, and Lapsus$.
This represents a strategic evolution from pure data extortion toward ransomware deployment capabilities, potentially increasing the group’s operational impact and revenue generation.
The platform’s development coincides with continued provocative public statements about planned attacks and customer data compromise operations.
Chatroom screenshots indicate sustained threats to leak additional corporate data, maintaining pressure on existing victims while signaling intent to prospective targets.
The group’s emphasis on identity-based access mechanisms particularly Active Directory credentials, cloud identity providers, and privileged administrative portals signals a deliberate focus on post-authentication exploitation and lateral movement capabilities.
This approach enables deeper network compromise before detection, extending dwell time and maximizing data exfiltration opportunities.
Security teams defending telecommunications, cloud service providers, software vendors, and large enterprise environments should prioritize strengthening insider threat detection protocols, implementing robust multi-factor authentication across privileged access pathways, and enhancing anomalous directory query monitoring.
The collective’s structured approach to initial access acquisition and commission-based recruitment model suggests insider-facilitated breaches will remain a primary attack vector throughout 2026.
Follow us on Google News, LinkedIn, and X to Get Instant Updates and Set GBH as a Preferred Source in Google.


