

There has been a warning from security experts about malware first identified as SMSFactory, an Android-based threat. Through the malware, the victims are subscribed to premium services at an unnecessary cost, which is really expensive.
While Avast has not disclosed how many victims have been affected by the attack, there have been hundreds of attempts to infect Android devices utilizing its products across at least eight countries protected by Avast security software.
It is important to note that SMS Factory has more than one distribution channel, including advertisements like:-
- Push notifications
- Promotional pop-ups
- Videos promising game hacks
- Adult content access
Targets
In the period May 2021 to May 2022, SMFactory targeted over 165,000 Android users. While in this attack, most of the users are from the following countries:-
- Russia
- Brazil
- Argentina
- Turkey
- Ukraine
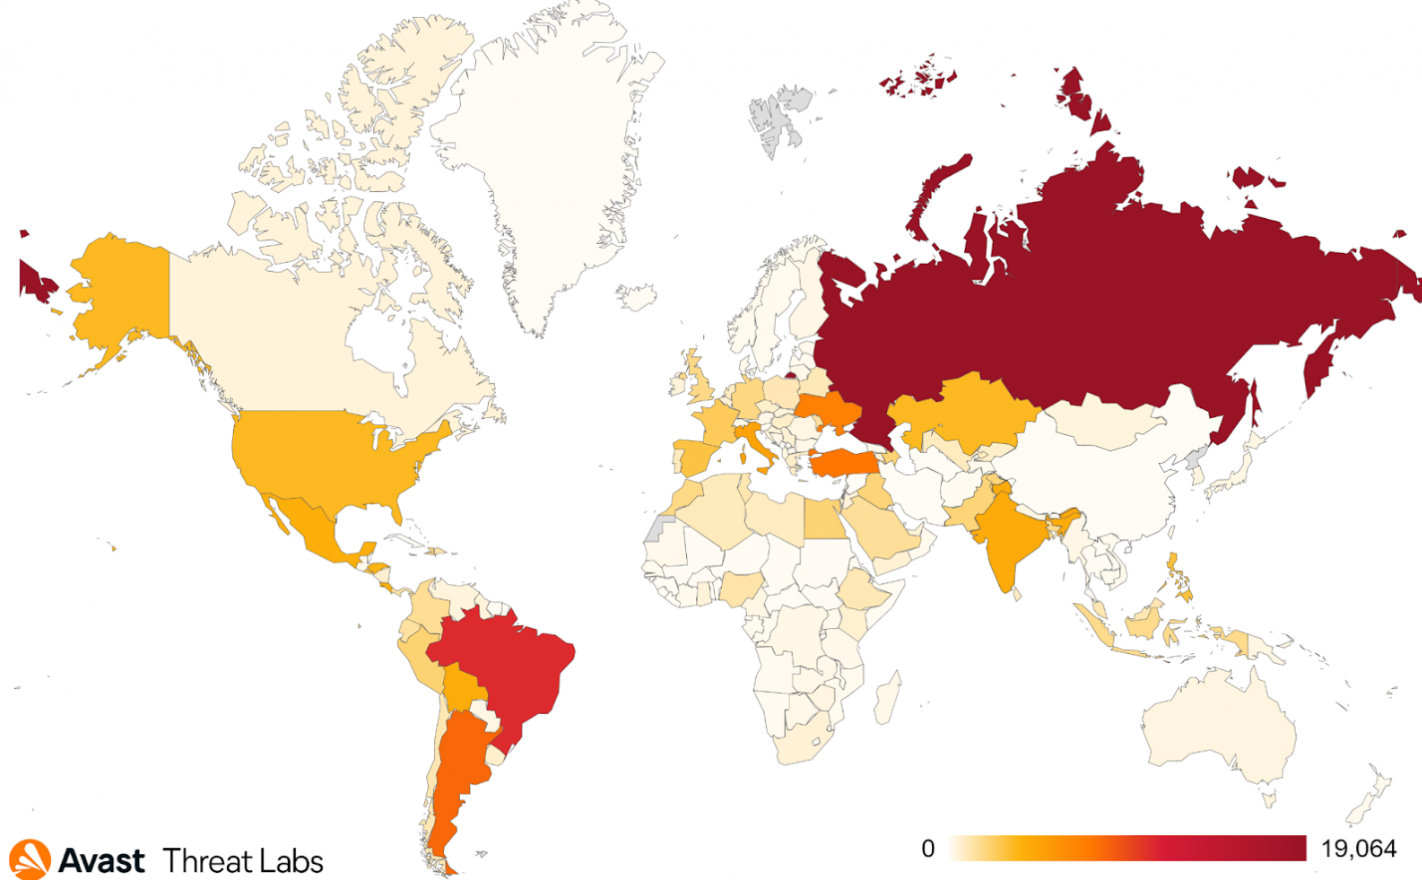
Sending premium SMS texts and making calls to premium phone numbers is the primary objective of SMSFactory.
One of Avast’s researchers noticed a new variant of malware that can also take advantage of compromised devices’ contact lists as well. There are many ways to distribute information, and among them, one of the main methods is to use compromised contact lists.
Further Analysis
The security experts on the case determined that SMSFactory is available on a number of unofficial app stores during the investigation. Moreover, the malicious APK package on APKMods and PaidAPKFree were also detected by the security analysts at ESET Security.
Various names may be associated with the SMSFactory APK. The first time it tries to install on the device, the Play Protect security system pops a warning message, and then it blocks the whole installation process.
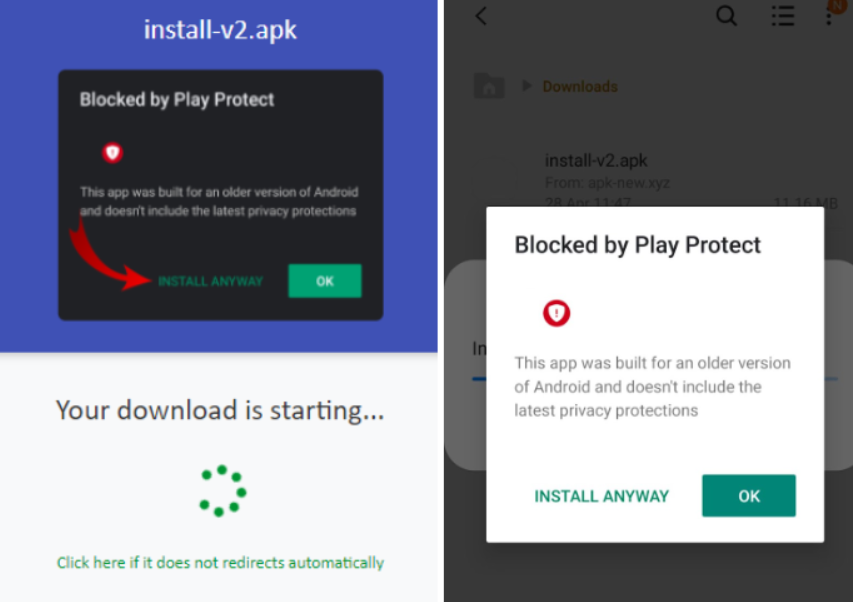
During installation, a number of permissions will be requested from the user, and here they are mentioned below:-
- Use of the entire screen
- Accessing location
- Make phone calls
- Send SMS
- Vibrate
- Track notifications
- Work from the background to begin activities
- Manage overlay
- Wake lock
Once it gets installed, then in the background, the SMSFactory continues all its operations. The SMSFactory establishes a connection with the infected device, and the ID profile of that device is sent over to the C2 server.
Recommendation
To avoid larger bills or to mitigate such situations the cybersecurity researchers have strongly recommended users follow the below-mentioned recommendations:-
- Don’t download any suspicious applications from untrusted sources.
- Before downloading any app, you should check all the reviews.
- Make sure that you always keep the minimum number of applications installed on your device.
- It is important that you keep your device updated at all times.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.







