

Google discloses security bug that affects Bluetooth Low Energy (BLE) version of the Titan Security Keys, non-Bluetooth security keys are not affected.
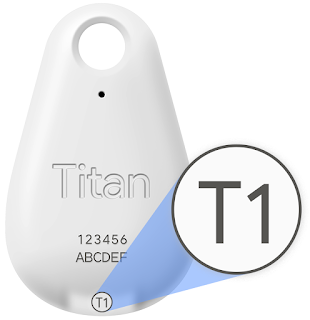
For the affected users, as an immediate measure, Google offering free replacement key. To check if you are affected, check the back of the key, if it has a “T1” or “T2” then your key is affected and your eligible for a free replacement.
Misconfiguration with Pairing Protocols
The bug is due to the misconfiguration in the Titan Security Keys Bluetooth pairing protocols, allows a hacker who is physically close which is approximately 30 feet can communicate with your key or with the device to be paired.
The Titan Security Keys provides an additional layer of security and protection against phishing. It supports all popular browsers.
According to Google with these two possible scenarios, an attacker could hijack the secret keys.
“When you’re trying to sign into an account on your device, you are normally asked to press the button on your BLE security key to activate it. An attacker in close physical proximity at that moment in time can potentially connect their own device to your affected security key before your own device connects. In this set of circumstances, the attacker could sign into your account using their own device if the attacker somehow already obtained your username and password and could time these events exactly.”
“Before you can use your security key, it must be paired to your device. Once paired, an attacker in close physical proximity to you could use their device to masquerade as your affected security key and connect to your device at the moment you are asked to press the button on your key. After that, they could attempt to change their device to appear as a Bluetooth keyboard or mouse and potentially take actions on your device.”
The primary function of the key, which is to protect the users against phishing attacks, is not affected. Google recommends users to replace the keys to minimize the risk.
As another possible, Google advised using the device in a private place where the potential attacker not within close physical proximity (approximately 30 feet).
Replacement can be requested for free by visiting google.com/replacemykey.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates also you can take the Best Cybersecurity courses online to keep your self-updated.
Related Read
Hackers Offered IoT Botnet as Service “TheMoon” : Botnet-as-a-Service
Hackers Exploiting ThinkPHP Vulnerability To Expand Hakai and Yowai Botnets
New Hacking Group Outlaw Distributing Botnet to Scan The Network & Perform







 version of the Titan Security Keys, non-Bluetooth security keys are not affected.)