

Researchers discovered 11 zero-day vulnerabilities dubbed “URGENT/11” in the most widely used operating system VxWorks, a Real-Time Operating System (RTOS) family.
VxWorks is Developed as proprietary software by Wind River Systems used in 2 billion devices including Firewalls, MRI machines, printers, SCADA devices and other areas such as critical infrastructure, networking equipment, medical devices, industrial systems, and even spacecraft, airplanes, trains.
Dubbed “URGENT/11,” vulnerabilities reside in the VxWorks’ TCP/IP stack (IPnet) over past 13 years and affected almost all version from 6.5.
Team of Researchers from Armis Labs uncovered these vulnerabilities and the company is known to disclose some of the critical bugs such as BLEEDINGBIT and BlueBorne, Bluetooth vulnerabilities that affected more than 5 billion devices.
Among 11 vulnerabilities, 6 of them are classified as “critical” and rest of the vulnerabilities classified as a denial of service, information leaks or logical flaws.
Nature of these vulnerabilities let attackers allow to remotely take over the vulnerable devices including industrial, medical and enterprise devices without any user interaction and also allows to bypass security devices such as firewall and NAT.
In order to exploit the critical system and bypass the security devices, attachers sending a specially crafted TCP Pocket and take complete control and it provides a gateway to control other systems by remotely broadcast the malicious packets.
URGENT/11 Vulnerabilities Attack Scenarios
Researchers described a 3 different type of attack scenarios that propose the significant risk to all of the impacted VxWorks connected devices and URGENT/11 can be used by an attacker to take control over a device in different situations
Scenario 1: Compromise the Network Defence bypass
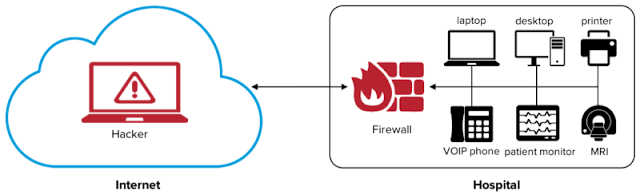
In the first scenario, vulnerable perimeter devices such as firewalls will take over by the attacker from the internet using the URGENT/11 vulnerabilities and an attacker can launch a direct attack to take over the complete control of the devices such as laptop, desktop, printers and more.
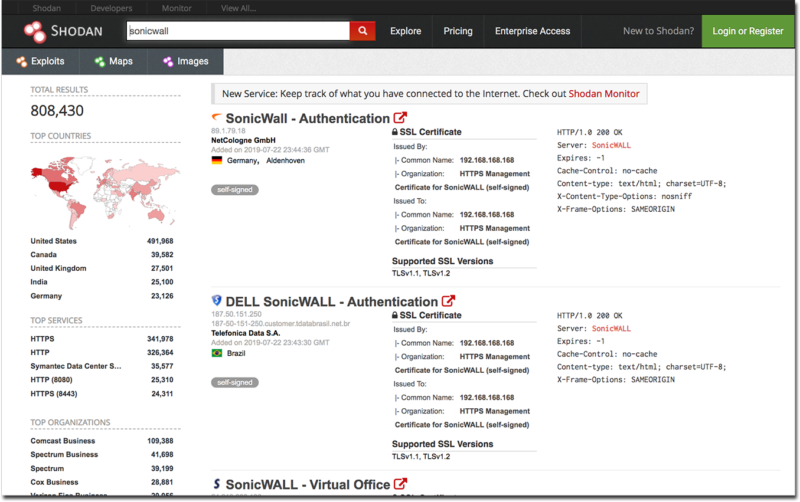
Let’s take a SonicWall firewall that runs on the vulnerable VxWorks OS as an example. and the shodan record shows over 808K SonicWall firewalls connected to the Internet.
Scenario 2: Network Bypassing Security From Outside
“Using URGENT/11 and an Internet connection, an attacker can launch a direct attack with a specially crafted TCP packet and take control over all firewalls at once and compromising all of the networks behind them.”
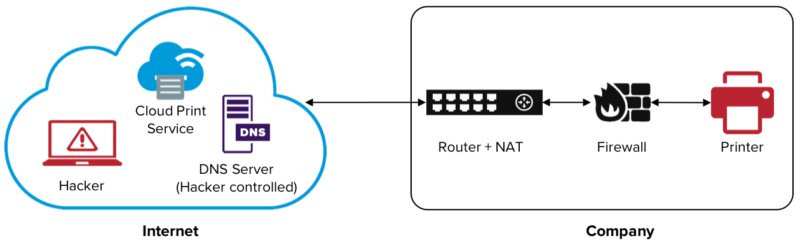
Similarly, Attackers compromise an IoT device connected to the cloud from within a secure network — such as a Xerox printer by intercepting the printer’s TCP connection to the cloud.
Scenario 3: Attack within the network
Attackers taking advantages of Prior attacks, send the targeted VxWorks device packets capable of taking full control over the device, without any form of user interaction.
For example, “a critical device that has only internal network connections: the patient monitor in a hospital. Even though it has no connection to the Internet, by infiltrating the network an attacker can nevertheless take it over. “
Affected Devices and Vulnerabilities
According to Armis Research, the URGENT/11 vulnerabilities affect all VxWorks versions since version 6.5, excluding versions of the product designed for certification, such as VxWorks 653 and VxWorks Cert Edition
The following list of devices is impacted by URGENT/11 vulnerabilities.
- SCADA devices
- Industrial controllers
- Patient monitors
- MRI machines
- Firewalls
- VOIP phones
- Printers
Following 6 Vulnerabilities allows attackers to perform remote code execution.
CVE-2019-12256 – Stack overflow in the parsing of IPv4 options
CVE-2019-12255 – memory corruption vulnerability
CVE-2019-12260 – memory corruption vulnerability
CVE-2019-12261 – memory corruption vulnerability
CVE-2019-12263 – memory corruption vulnerability
CVE-2019-12257 – Heap overflow in DHCP
5 Vulnerabilities allow attackers to perform a denial of service, information leak or certain logical flaws.
CVE-2019-12258 – TCP connection DoS via malformed TCP options
CVE-2019-12262 – Handling of unsolicited Reverse ARP replies
CVE-2019-12264 – Logical flaw in IPv4 assignment by the ipdhcpc DHCP
CVE-2019-12259 – DoS via NULL dereference in IGMP parsing
CVE-2019-12265 – IGMP Information leak via IGMPv3 specific membership report.
You can also read the complete technical details of these vulnerabilities here in White Paper.
Armis has been reported all the vulnerabilities to Wind River®, the maintainer of VxWorks, and the latest VxWorks 7 released on July 19 contains fixes for all the discovered vulnerabilities.
Sponsored: Download Free GDPR Comics Book – Importance of Following General Data Protection Regulation (GDPR) to protect your Company Data and user privacy
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity updates also you can take the Best Cybersecurity course online to keep yourself updated.







