The Volcano Demon group has been discovered spreading a new ransomware called LukaLocker, which targets Idealease Inc., a truck leasing company.
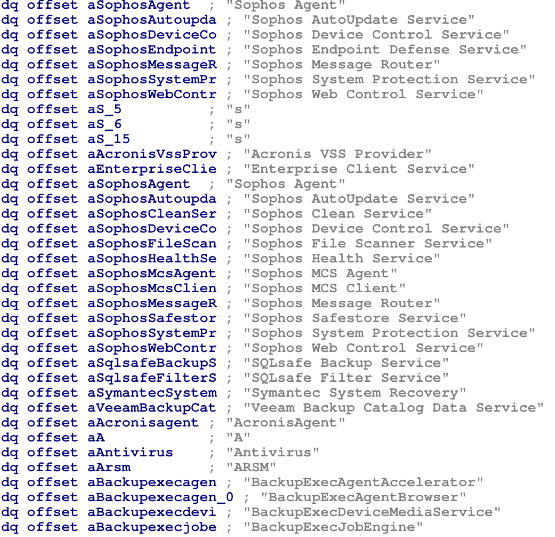
The malware targets several security, monitoring, and backup services, including antivirus software like Trend Micro, Malware Bytes, Sophos, and McAfee.
The malware disables the service if any of these are found on the machine.
In recent weeks, Volcano Demon has been claimed to have carried out several profitable cybercrime attacks. It specifically targets the industrial and logistic sectors.
Particularly, the leadership of the victim organization is intimidated and negotiated for payments by the group over the phone.
Are you from SOC/DFIR Teams? - Sign up for a free ANY.RUN account! to Analyse Advanced Malware Files
Behaviors Spotted in the Attack
The malware is coded in C++ and is presented as an x64 binary. By using dynamic API resolution and API obfuscation to conceal its destructive capabilities, the LukaLocker ransomware avoids detection, analysis, and reverse engineering.
A command prompt window that opens when the malware is executed displays a list of the processes that it tries to terminate.
After this operation is completed, the system encrypts files and appends “.NBA” to their filenames. It then saves readme.txt to the desktop.
“Your corporate network has been encrypted. And that’s not all – we studied and downloaded a lot of your data, many of these have confidential status”, reads the ransom note.
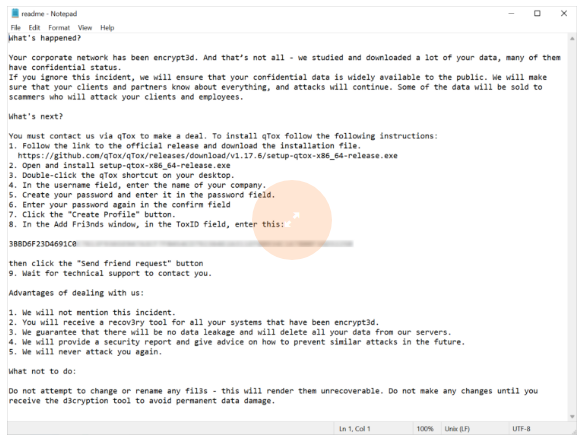
In this case, the ransom note specifies that to retrieve files, you must speak with the operator via the qTox encrypted chat client. An instant chat app called qTox is designed to avoid government surveillance.
“Various security, monitoring and backup services are targeted. This includes antivirus software such as Malware Bytes, Sophos, McAfee and Trend Micro”, reads the SonicWall threats research report.
“If any of these are present on the system, the service is disabled by the malware”.
The Volcano Demon operators usually encrypt the data of their victims before reaching out to them. The gang then notifies its victims that their files have been effectively compromised by leaving a ransom note.
After then, the attackers will begin pushing their victims into complying with their requests to commence their extortion scheme. These threat actors will threaten to tell clients and partners and carry out more attacks if their victims don’t address the problem.
The actors would also threaten to sell the employees’ and clients’ data to scammers if the infiltrated organizations don’t comply.
Ransomware operators are shifting their tactics; recently, a large number of new threat actors have emerged and begun targeting different types of enterprises.
Businesses should strengthen their security protocols since malicious actors will always find new ways to get into networks and steal information.
“Is Your System Under Attack? Try Cynet XDR: Automated Detection & Response for Endpoints, Networks, & Users!”- Free Demo