
Aeternum operators are abusing Polygon smart contracts as a decentralized dead-drop resolver, allowing malware to retrieve and rotate command-and-control (C2) domains without depending on conventional attacker-owned servers.
The approach turns a public blockchain into resilient C2 infrastructure that is substantially harder to disrupt through domain seizures, hosting takedowns, or sinkholing.
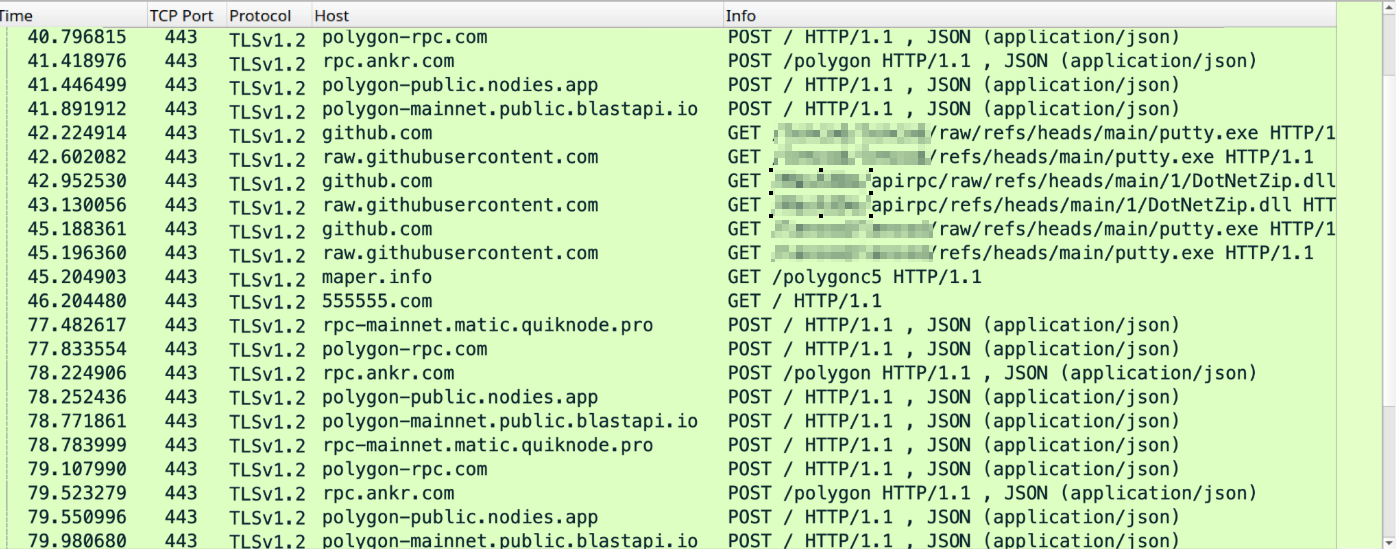
Rather than contacting a fixed hostname, an infected device submits an eth_call request containing a contract address in the to field and the function selector 0xb68d1809 in the data field.
That selector maps to a getDomain() routine that returns an encrypted or plaintext command payload.unit42.
The method creates a resilient control plane. Polygon RPC services are legitimate, public, and widely available, so blocking one endpoint does not eliminate the malware’s ability to reach the contract.
The loader can query alternate RPC providers and retrieve updated infrastructure from the same on-chain source.
In one analyzed case, the loader communicated with 22 different contract addresses, underscoring how operators can distribute and refresh their control infrastructure.
The key operational capability is an administrative smart-contract method identified as 0xb249cd2d, or updateDomain().
Operators with the deployer wallet can invoke it to overwrite the stored C2 value, pushing a replacement domain to infected hosts without rebuilding or redistributing the loader.
A public getDomain() function then exposes the updated value to bots polling the contract.
Researchers linked activity to a smart-contract architecture that stores an administrator wallet address and encrypted domain data in separate storage slots.
The contracts also retain an additional selector, 0xf851a440, while maintaining the same state-management model across deployments.
Changes in Solidity compiler versions, from solc 0.8.0 through 0.8.30, suggest ongoing development and redeployment rather than a one-off proof of concept.
This design gives the operators a rapid contingency mechanism. If a C2 domain is blocked, exposed, or seized, they can publish another value on-chain and wait for infected systems to poll again.
The blockchain record may be transparent, but its globally replicated nature complicates traditional infrastructure removal.
Unit42 said in a report shared with GBhackers, Aeternum, marketed as an “Aeternum C2 BotNet Loader,” is a C++-based Windows malware family that uses public Polygon JSON-RPC endpoints to read commands embedded in smart-contract storage.
Aeternum’s encryption is less sophisticated than its infrastructure. The loader uses PBKDF2-HMAC-SHA256 and AES-GCM to decrypt returned payloads, but researchers found a self-salting design in which the password is reused as the salt.
Because the contract address and encrypted response are observable, analysts can reproduce the decryption process and recover commands.
Aeternum Use Polygon Smart Contracts
One recovered instruction used the format all:url:<URI>, directing compromised hosts to fetch a payload.
However, not every operation requires encryption: related samples returned hexadecimal data that decoded directly into a Pastebin raw URL containing XMRig configuration data.
This shows Aeternum can combine blockchain-based routing with commodity hosting services for second-stage configuration and payload delivery.

The Aeternum ecosystem includes more than a blockchain-aware loader. One campaign delivered a legitimate PuTTY installer alongside a malicious DotNetZip.dll retrieved from GitHub repositories.
An outbound connection HTTP POST request to a C2 server at 193.221.200[.]219 with a custom user-agent (cpp-httplib/0.18.3) and JSON values containing two keys with Base64-encoded values.
The DLL collected host information and exfiltrated it through Telegram’s Bot API, using hard-coded bot credentials and a chat identifier.
A separate sample, a PyInstaller-packed executable, deployed both XWorm RAT and XMRig.

The miner configuration included evasive settings designed to suspend mining when monitoring tools run and terminate processes associated with endpoint protection or competing resource-intensive software.
Researchers also analyzed Python-based source code masquerading as a DBeaver installer. The code checks for virtualized or sandboxed environments, validates at least 8 GB of memory, establishes Startup-folder persistence, and uses Early Bird APC injection against a suspended signed binary.
It also targets cryptocurrency data, including browser-extension and desktop-wallet information, before sending reconnaissance through Telegram.
Defenders should monitor outbound JSON-RPC eth_call traffic to Polygon RPC endpoints, particularly requests carrying selector 0xb68d1809.
They should also inspect for 0xb249cd2d activity during threat-hunting and correlate blockchain queries with suspicious GitHub, Pastebin, Telegram API, or newly registered-domain traffic.
On endpoints, high-signal behaviors include UPX-packed C++ binaries creating randomly named Startup shortcuts, suspicious AppData\Local copies, anti-VM checks, dpapimig.exe process injection, and outbound Telegram sendDocument requests.
Aeternum demonstrates that blockchain C2 is no longer merely an evasion novelty: it is an operationally viable mechanism for rotating malware infrastructure while preserving low cost and takedown resistance.
IOCs
| Type | Value | Description |
| SHA256 hash | 5bfb25b8255b61e5ffdf6804451534bcfa9f1dfd225e6c8cdcefb5f50d846898 | Aeternum C++ loader executable |
| SHA256 hash | 1505eda3da68e2ff9919b55a31018bd30a991236f041aee835f3bc4e430ce505 | Malicious downloaded DotNetZip.dll |
| Filename | DotNetZip.dll | Malicious payload executed by the loader |
| Filename | putty.exe | Benign file downloaded for testing/staging |
Note: IP addresses and domains are intentionally defanged (e.g., [.]) to prevent accidental resolution or hyperlinking. Re-fang only within controlled threat intelligence platforms such as MISP, VirusTotal, or your SIEM.
★ Which Security Tools Should You Cut? Score Them on One Page – Download the Inherited Security Stack Guide







 domains.)