Sunday, October 18, 2026

Turla Group Updated ComRAT Malware to Use Gmail web Interface for Command and Control

The ComRAT malware is a remote administration tool and is used by the Turla hacker group. It was first spotted in November 2014. The Trula hacker group is active for more than ten years.

ComRAT malware also known as Agent.BTZ, the first version of it was released in 2007. It becomes infamous after it was used to breach the US military in 2008.

Turla’s operators known for maintaining a large arsenal of malware includes a rootkit, several complex backdoors aimed at different platforms, including Microsoft Exchange mail servers, and a large range of tools to enable pivoting on a network.

ComRAT Malware

A new variant of ComRAT malware found by researchers in 2017 and it is active as recently as January 2020. Three targets were identified; two of them are ministries of Foreign Affairs and a national parliament.

The main use of the ComRAT malware is to steal confidential documents, in one such case researchers observed that “deployed a .NET executable to interact with the victim’s central MS SQL Server database containing the organization’s documents.”

In addition to document stealing the hacker group runs various commands to gather information about services such as “Active Directory groups or users, the network, or Microsoft Windows configurations such as the group policies.”

ComRAT Malware
ComRAT Malware Operation

The most recently compiled ComRAT malware dated November 2019, according to the ESET telemetry, the malware was installed using an existing foothold such as compromised credentials or via another Turla backdoor.

All the files associated with ComRAT are stored in a Virtual File System and the VFS is encrypted using AES-256 in XTS mode.

Two Command and Control channels

  • HTTP – The malware makes HTTP requests to its C&C server.
  • Email – Uses the Gmail web interface to receive commands and exfiltrate data
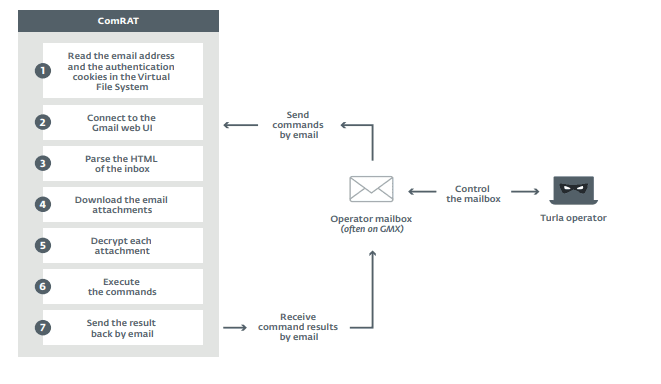
Gmail used for C&C

The most interesting feature with the new version of the malware uses the Gmail web UI to receive commands and exfiltrate data.

So that attackers can bypass some security solutions as the communication not from the malicious domains. Eset published a detailed report with Indicators of compromise.

You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.

Gurubaran
Gurubaran
Gurubaran is a co-founder of Cyber Security News and GBHackers On Security. He has 10+ years of experience as a Security Consultant, Editor, and Analyst in cybersecurity, technology, and communications.

Hot this week

How To Access Dark Web Anonymously and know its Secretive and Mysterious Activities

What is Deep Web The deep web, invisible web, or...

How to Build and Run a Security Operations Center (SOC Guide) – 2023

Today’s Cyber security operations center (CSOC) should have everything...

Russian Hackers Bypass EDR to Deliver a Weaponized TeamViewer Component

TeamViewer's popularity and remote access capabilities make it an...

Web Server Penetration Testing Checklist – 2026

Web server pentesting is performed under three significant categories: identity,...

ATM Penetration Testing – Advanced Testing Methods to Find The Vulnerabilities

ATM Penetration testing, Hackers have found different approaches to...

Hackers Use ConnectWise SkyKick Credentials to Access Microsoft 365, Halting Cloud Backups

Attackers abused compromised ConnectWise Cloud Backup credentials to access...

Anthropic’s Claude AI Uncovers Origins of NSA-Provided Cryptographic Keys After 25 Years

Anthropic says an internal Claude research model reconstructed how...

OpenBSD Kernel Flaw Dating Back 37 Years Enables Local Privilege Escalation to Root

A newly disclosed OpenBSD kernel exploitation chain combines a...

GhostAction Hackers Hide Credential-Stealing Malware in Fake Font Files Across 94 GitHub Repositories

GhostAction attackers have expanded their GitHub credential theft campaign...

SideCopy Hackers Target Indian Organizations With ReverseRAT Malware to Steal Data

Indian authorities have warned that SideCopy hackers are targeting...

New GhostBat Android Malware Targets 60 Banking and UPI Apps to Steal PINs

A new GhostBat RAT variant targets 60 Android financial...

New ROMULUS Malware Platform Uses Six Servers to Deliver Multiple Malicious Payloads

ROMULUS, a shared ClickFix delivery platform operating across six...

Related Articles

Recent News


