

The security analysts from the cybersecurity firm Bitdefender have recently noted the new backdoor BADHATCH malware that was being used by the very well-known threat actor, FIN8.
However, this is not the first time that FIN8 has been initiating any attack, as per the report these APT threat actors were targeting victims since 2016.
Well, this APT group is famous for taking elongated breaks to adjust their methods, and procedures (TTP) as it helps them to boosts their success rate.
Tried and True Methods of FIN8
The APT group FIN8 always targets the financial services, as well as the POS systems, which are the main targets of this group. Apart from this the FIN8 generally uses built-in tools and interfaces, so that they can easily misuse legal services such as sslip.io.
FIN8 is very famous for its defined capabilities, it has a mixture of such abilities and that’s what makes it a strong and dangerous APT group.

All the operations that are implemented by the threat actors of the FIN8 group are very professional, thus the experts have claimed that sometimes it becomes quite difficult to identify the threat.
Analysis of an Attack
The security researchers are yet not clear about all the details of this malware, but they are trying to think about a conclusion based on the previous attacks that were initiated by the FIN8 group.
However, after so many examinations, it’s quite clear that the FIN8 APT group mostly prefers the methods that were generally used by the engineer.
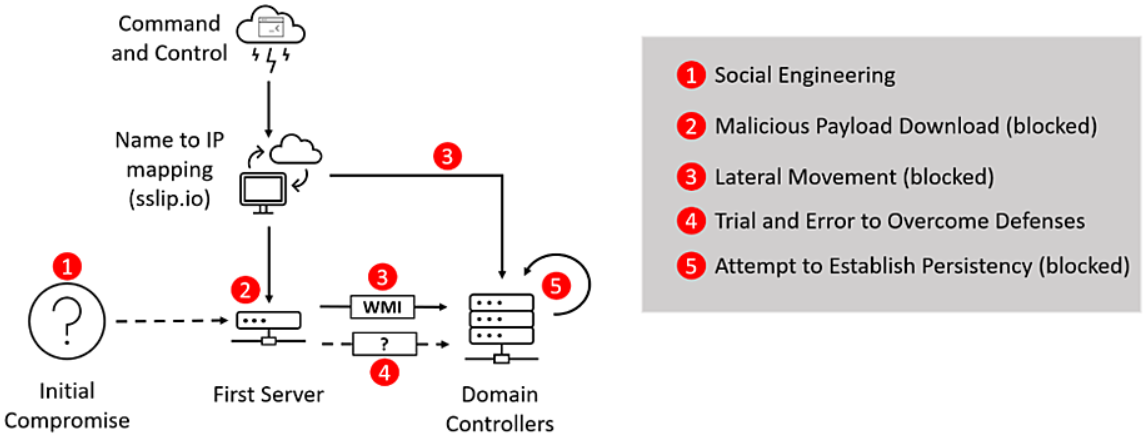
Network Reconnaissance and Lateral Movement
After a long investigation, it has been clear that in this attack at least two user accounts were negotiated by the threat actors. However, the analysts have noted the very first indication of a compromise that was caught on one of the database servers.
Not only this during the attack the threat actors were also engaged in network reconnaissance and regained a list of conferred domains as well as a list of domain controllers that have the commands we have mentioned below:-
- nltest.exe /domain_trusts
- nltest.exe /dclist:<domain>
Once the initial reconnaissance has been done, the threat actors scattered all over the network and start developing their space by targeting domain controllers. However, the threat actors also get engaged in lateral movement by utilizing the WMIC utility for remote code execution.
Recommendations
Apart from this, the cybersecurity authorities have suggested some recommendations that are to be followed carefully, as they will surely reduce the impact of financial malware:-
- At first, separate the POS network from the ones that were being used by the employees or guests
- After that start the cybersecurity awareness training for employees, as it will help them detect phishing e-mails.
- Next tune the e-mail security solution to automatically discard malicious or unusual attachments.
- Combine the threat intelligence into current SIEM or security controls for proper Indicators of Agreement.
- Lastly, the organization that does not have a strong security team should go for the outsourcing security
Moreover, the organizations must follow all the recommendations that are suggested by the security executives to stay strong and to keep themselves safe from such attacks.
Follow us on Linkedin, Twitter, Facebook for daily Cybersecurity News & Updates







