

A new clicker malware found in Google play dubbed Haken aims to gain control over the affected devices and to generate illegitimate profit.
Checkpoint researchers observed the new malware family while looking for another clicker malware BearClod.
The Haken malware is capable of exfiltrating sensitive user data from the infected device and also subscribes to premium services.

Eight such apps caught distributing the malware in the Google play store, altogether downloaded for more than 50,000 times.
Haken Clicker Malware
To perform clicking malware utilizes the native code and injection to Facebook and AdMob libraries while communicating to the server.
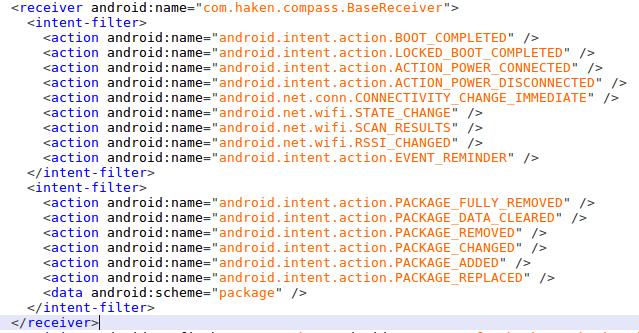
The first entry point for the backdoored app is Haken clicker receiver called ‘BaseReceiver’ which seeks permission from the user to make the application run once the device is started.
According to Checkpoint report “the BaseReceiver loads a library kagu-lib which calls a method called ‘startTicks’ which after inspection calls the method ‘clm’ from ‘com/google/android/gms/internal/JHandler.”
This particular class registered two workers and a timer, one worker communicates with the C&C server to download the configuration and process it.
The second worker triggered by the timer, responsible for “injects code into the Ad-related Activity classes of well-known Ad-SDK’s like Google’s AdMob and Facebook”.
By injecting the clicking functionality the attackers able to mimic the user clicks to generate illegitimate revenue.
The affected apps have been reported to Google by Checkpoint and the affected applications removed from Google play.
Following are the apps
| Package Name | Installs | Sha256 |
| com.faber.kids.coloring | 10,000+ | 381620b5fc7c3a2d73e0135c6b4ebd91e117882f804a4794f3a583b3b0c19bc5 |
| com.haken.compass | 10,000+ | 30bf493c79824a255f9b56db74a04e711a59257802f215187faffae9c6c2f8dc |
| com.haken.qrcode | 5,000+ | 62d192ff53a851855ac349ee9e6b71c1dee8fb6ed00502ff3bf00b3d367f9f38 |
| com.vimotech.fruits.coloring.book | 5,000+ | f4da643b2b9a310fdc1cc7a3cbaee83e106a0d654119fddc608a4b587c5552a3 |
| com.vimotech.soccer.coloring.book | 5,000+ | a4295a2120fc6b75b6a86a55e8c6b380f0dfede3b9824fe5323e139d3bee6f5c |
| mobi.game.fruit.jump.tower | 100+ | e811f04491b9a7859602f8fad9165d1df7127696cc03418ffb5c8ca0914c64da |
| mobi.game.ball.number.shooter | 50+ | d3f13dd1d35c604f26fecf7cb8b871a28aa8dab343c2488d748a35b0fa28349a |
| com.vimotech.inongdan | 50+ | a47049094051135631aea2c9954a6bc7e605ff455cd7ef1e0999042b068a841f |
Google announced that nearly 600 apps removed from the Google Play Store and banned from ad monetization platforms.
These apps are removed for showing disruptive ads that displayed to users in unexpected ways and for out-of-context ads in which developers serve ads even if the user not active with the application.
Follow us on Twitter, Linkedin, Facebook for Daily cyber security & hacking news updates.


