

Hackers opt for DLL hijacking as a technique to exploit vulnerable applications because it allows them to load malicious code by tricking a legitimate application into loading a malicious DLL.
This can give them unauthorized access and control over a system or application, enabling various types of attacks like:-
- Privilege escalation
- Data theft
- System compromise
An active threat involves an Infostealer distributing a legitimate EXE file alongside a hidden malicious DLL in the same directory.
The legitimate EXE runs the malicious DLL, a technique known as DLL hijacking, commonly used for malware distribution.
Malicious DLL With Legitimate EXE Files
Malware posing as software cracks is growing at a rapid pace and is getting distributed by the threat actors using DLL hijacking.
Users searching for cracked software leads to malicious sites, and the downloads are encrypted RAR files with passwords.
Running EXE infects the system, and they often have valid signatures, so always be cautious with cracked software, reads the ASEC report.
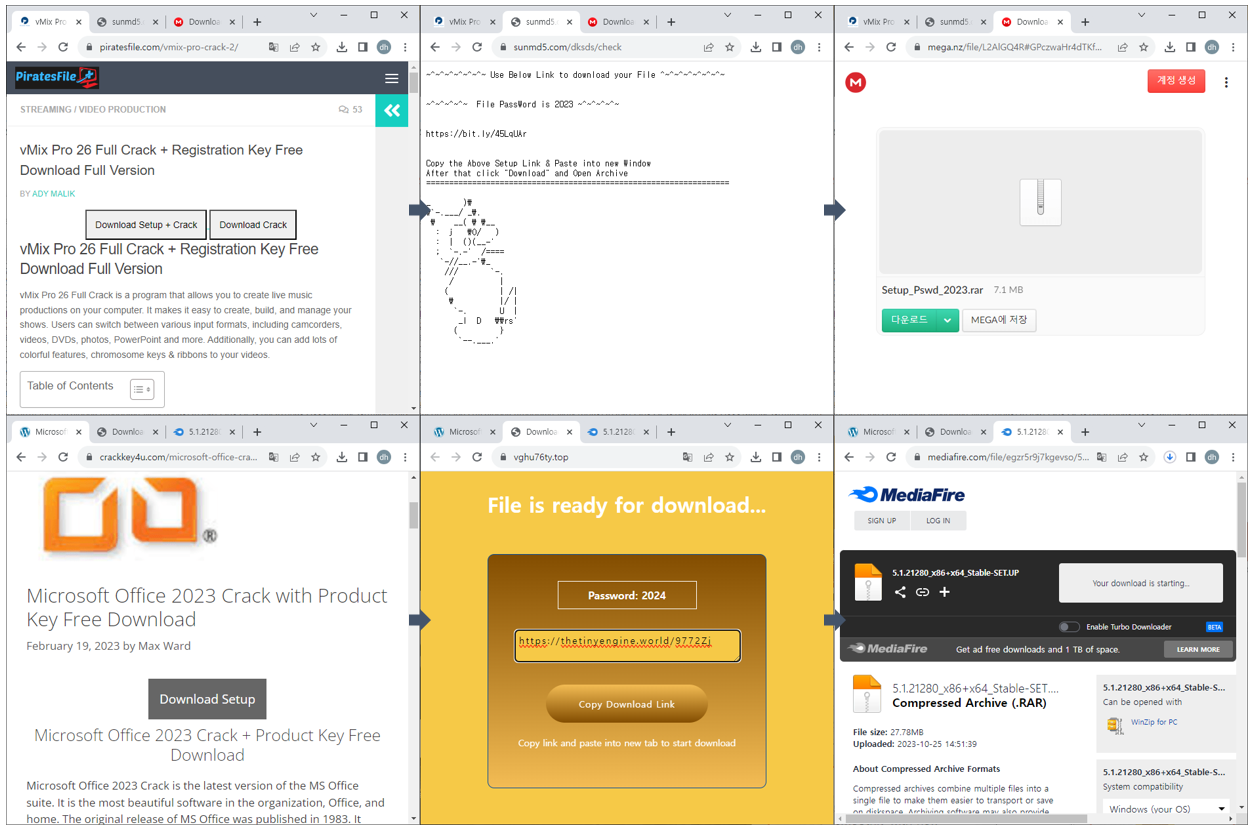
Malicious DLLs tweak part of legitimate DLLs as they decrypt and run data from a nearby file. Hiding data this way avoids altering DLL appearance, reducing detection risk.
For malware to work, the following elements are required to be placed in the same folder:-
- Data
- EXE
- Modified DLL
Unzipping the password-protected file with the code “2023” gives you the following files:-
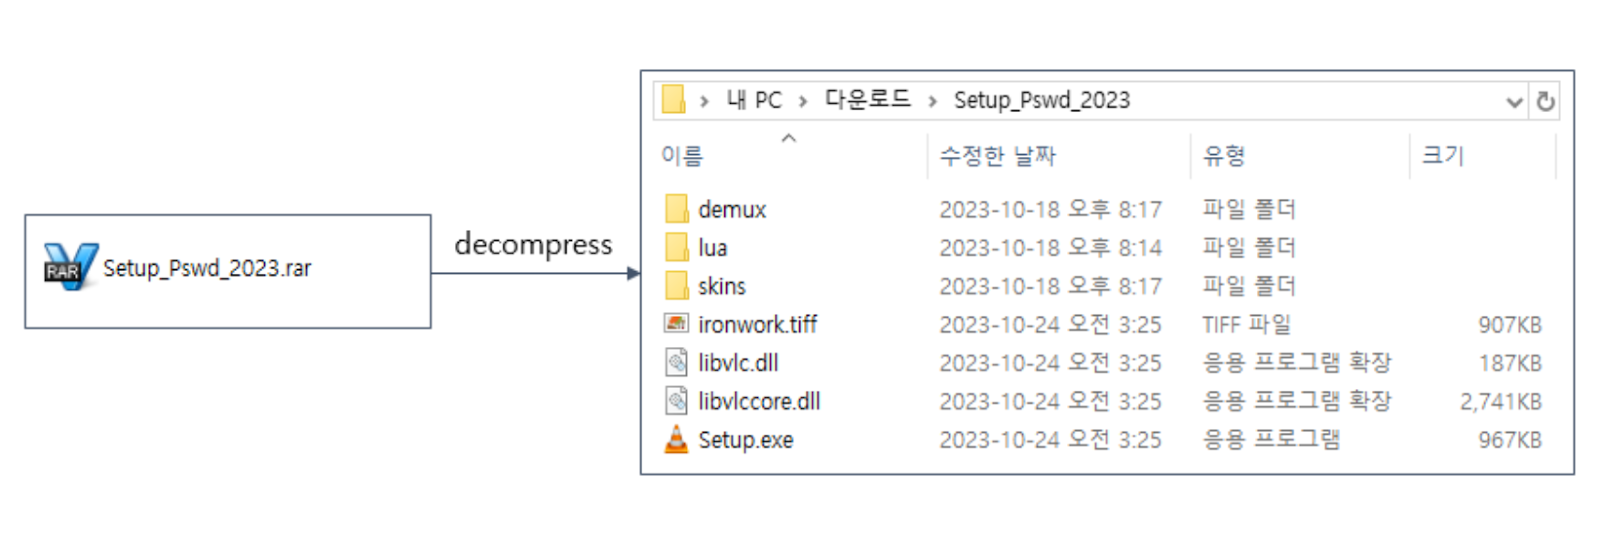
The following two files are genuine VLC files with valid signatures:-
- Setup.exe
- libvlc.dll
The “libvlccore.dll” is altered and lacks a matching signature, due to which the extra directories like demux and lua serve to mask its malicious nature.
Running ‘Setup.exe’ activates ‘libvlccore.dll,’ triggering a modified function that reads and decrypts ‘ironwork.tiff’ in the same folder. This file holds code info. disguised as a PNG.
It loads “pla.dll” from SysWow64 and injects code into its memory differently than typical malware. This method uses NTDLL relocation, and for “cmd.exe,” it loads “pla.dll” and injects the malware into it.
A data file is written to %TEMP%. cmd.exe inherits it and has its EntryPoint changed to “pla.dll” code. This code decrypts a file, generates LummaC2 malware, and runs “explorer.exe,” injecting and executing the binary.
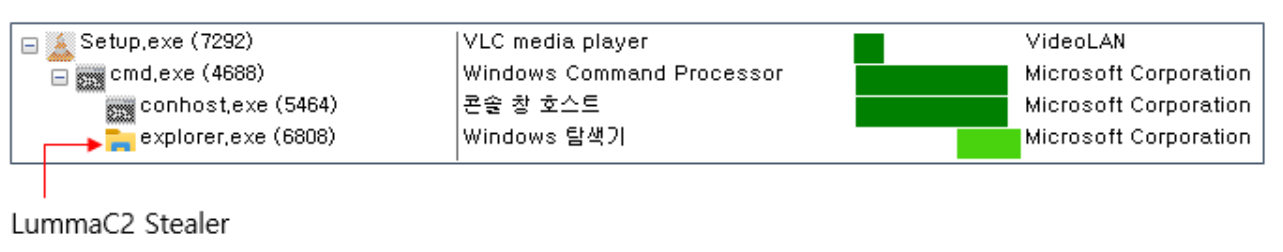
LummaC2 targets victims and installs malware from its C2 server, and it steals various sensitive data using JSON-formatted responses from C2.
The malware infects via legitimate EXE files, looking like original DLLs, posing a low detection risk.
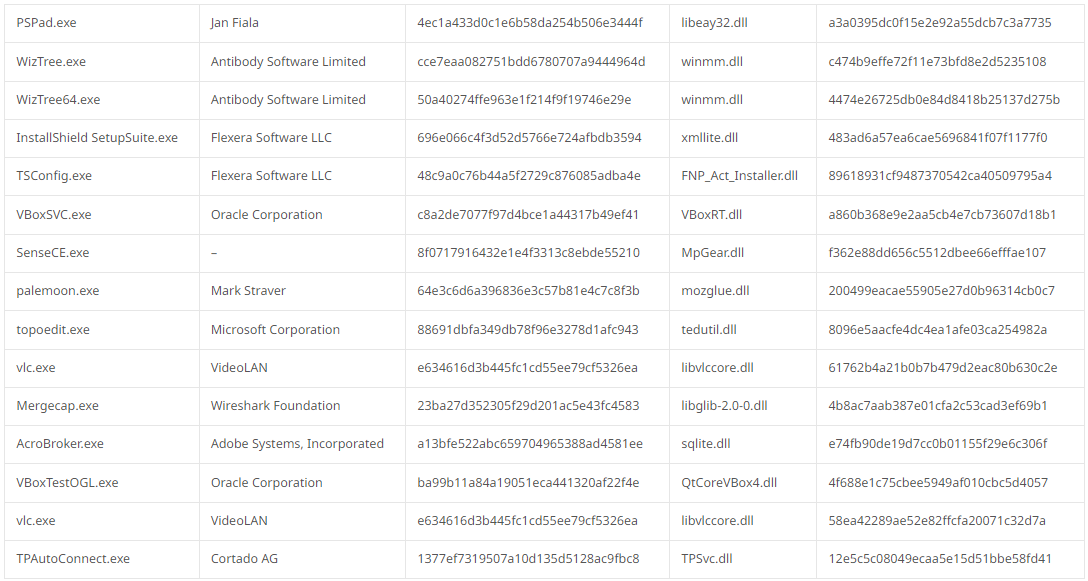
IOCs
Protect yourself from vulnerabilities using Patch Manager Plus to patch over 850 third-party applications quickly. Try a free trial to ensure 100% security.


