

Researchers observed a stealthy Android malware poses as ad blocker serves full-screen ads while opening the browsers, in the notification section and home widgets.
The malicious app(Ads Blocker V3.9) infection is on the rise, Malwarebytes researchers able to obtain 1,800 samples through their Mobile Intelligence System which shows the infection rate is high.
Good news is the app not distributed from Google play, still, the source of infection is unknown and it targets mainly the users in the united states and also in European countries such as France and Germany.
Trouble Starts Right After Installation
After the installation straightaway, the app asks to Allow display over other app rights form the users, once it granted then it shows a fake popup asking for the Connection request.

For an adblocker app, why it requires to connect with a VPN service? yes, it is a fake popup to make the malware run the malware all the time in the background.

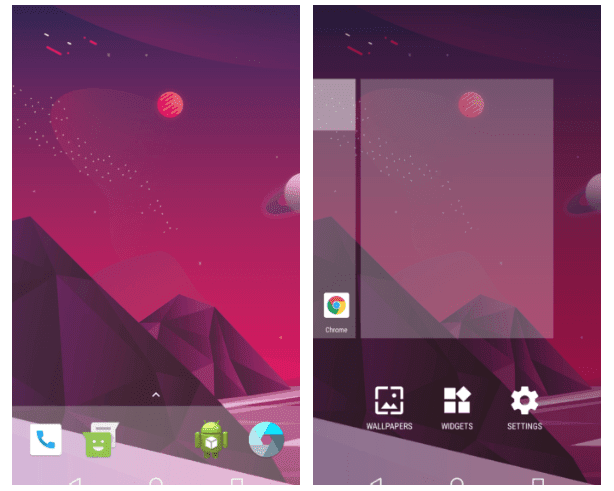
Next, it asks to add a home screen widget, once added it hides and the widget is nowhere found. Nathan Collier who analyzed the malware managed to find the widget on a new home screen page.
To make it legit it also includes some jargon codes, once the app installed no icons will be created and it is hard to find. The only clue is the blank white notification and the small key icon status bar.

“If you try to find Ad Blocker on the App info page on your mobile device to remove manually, it once again hides with a blank white box. Also if you click on the blank screen it may lead to uninstall other malware, reads Malwarebytes report.”
Ads Everywhere
It shows ads in all possible places of devices, starting from the basic full-page ad, ads in notifications, ads in the default browser and with the home screen.

Researchers believe that Ads Blocker V3.9 is more stealthy than xHelper and is capable of reaching the same rate of infection.







