

Researchers discovered a new cyberespionage campaign named Project Spy through which hackers targeting Android and iOS devices with spyware using Coronavirus Update App.
Cybercriminals taking advantage of the currently ongoing COVID-19 pandemic as a lure and lunching a fake Coronavirus updates App and install spyware on the victim’s devices.
We have reported several ongoing malware and phishing campaigns related to Coronavirus pandemic targeting billions of mobile users every day.
“Attackers who behind this malware are amateurs and the spyware contains incomplete iOS codes used in this campaign may have been bought while other capabilities appear to have been added.” Trend Micro researchers said.
Project Spy Activities and Capabilities
Researchers observed this mobile spyware campaign at the end of the March, and the Corna virus update app masquerading and tempt users to download and install it on their device.
The Project Spy has installed with various data-stealing capabilities that include capable of stealing messages from popular messaging apps by gaining permission from the users.

It also requests permission to access the storage and abusing notification permissions to read the notification content.
There are following data collection activities are observed:-
- Upload GSM, WhatsApp, Telegram, Facebook, and Threema messages
- Upload voice notes, contacts stored, accounts, call logs, location information, and images
- Upload the expanded list of collected device information (e.g., IMEI, product, board, manufacturer, tag, host, Android version, application version, name, model brand, user, serial, hardware, bootloader, and device ID)
- Upload SIM information (e.g., IMSI, operator code, country, MCC-mobile country, SIM serial, operator name, and mobile number)
- Upload wifi information (e.g., SSID, wifi speed, and MAC address)
- Upload other information (e.g., display, date, time, fingerprint, created at, and updated at)
Researchers also observed another 2 earlier versions of the Corona Virus Update app detected in May 2019.
The first version of Corona update app has limited capabilities of following:-
- Collect device and system information (i.e., IMEI, device ID, manufacturer, model and phone number), location information, contacts stored, and call logs
- Collect and send SMS
- Take pictures via the camera
- Upload recorded MP4 files
- Monitor calls
In the second version appeared as Wabi Music, and copied a popular video-sharing social networking service as its backend login page.
This version also has a similar version of similar capabilities to the first version of the following;-
- Stealing notification messages sent from WhatsApp, Facebook, and Telegram
- Abandoning the FTP mode of uploading the recorded images
The developer’s name listed was “concipit1248” in Google Play, and the researchers check with the same code on the App store and found two other apps that targeted the app store.
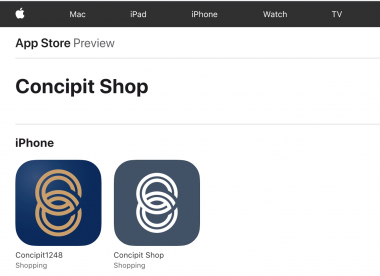
According to Trend Micro research ” the “Concipit1248” app requested permissions to open the device camera and read photos, the code only can upload a self-contained PNG file to a remote server. This may imply the “Concipit1248” app is still incubating”.
Currently ongoing this Cyberespionage installed this Corona virus update spyware app on several country users devices including Pakistan, India, Afghanistan, Bangladesh, Iran, Saudi Arabia, Austria, Romania, Grenada, and Russia.
You can follow us on Linkedin, Twitter, Facebook for daily Cybersecurity and hacking news updates.
Indicators of Compromise
| e394e53e53cd9047d6cff184ac333ef7698a34b777ae3aac82c2c669ef661dfe |
| e8d4713e43241ab09d40c2ae8814302f77de76650ccf3e7db83b3ac8ad41f9fa |
| 29b0d86ae68d83f9578c3f36041df943195bc55a7f3f1d45a9c23f145d75af9d |
| 3a15e7b8f4e35e006329811a6a2bf291d449884a120332f24c7e3ca58d0fbbd |





